❌

Reading view

‘I felt disgusted’: MEP speaks out over nude deepfakes and urges EU action

Lena Schilling of Austrian Greens says images are ‘digital violence against women’ and a threat to democracy

An Austrian MEP has spoken out about her experience of being “stripped naked” online without her consent and has urged the EU to take action, as a report found that one in six female MEPs had been targeted by sexualised AI-generated content.

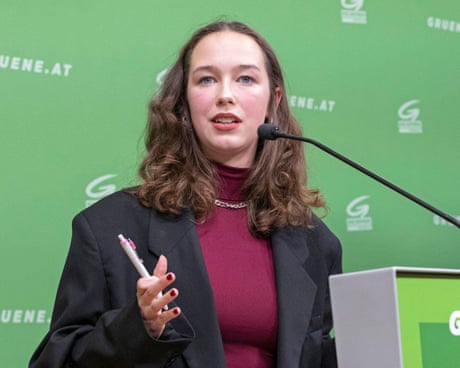
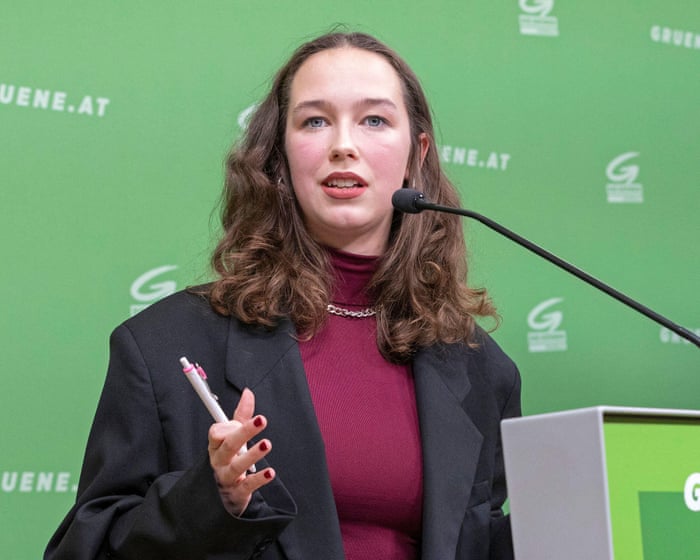
Lena Schilling of the Green party said she had learned last month about nude deepfakes of herself circulating online. When she opened the links, she found herself staring at images from one of her first ever press conferences – but the images had been digitally altered to remove her clothing.

Continue reading...

© Photograph: APA-Images/Alamy

© Photograph: APA-Images/Alamy

© Photograph: APA-Images/Alamy

  •  

Fake Linda and me: the Agatha Christie-worthy mystery of the fraudster who stole my byline

How a string of bizarre events led writer Linda Geddes to don her sleuthing cap and dig into a world of shadowy impersonators

It started with an entirely ordinary interaction on LinkedIn. Someone had tagged me in a post, saying how much they’d enjoyed contributing to a New York Post article I’d written about “chronoworking”. As the author of a book about circadian rhythms, it was exactly the sort of subject I might write about. Except I’d never heard of this person, let alone interviewed them.

I clicked on the link and my stomach dropped. There, above an article about people who organise their working lives around their biological clocks, was my name: Linda Geddes.

Continue reading...

© Photograph: Adrian Sherratt/The Guardian

© Photograph: Adrian Sherratt/The Guardian

© Photograph: Adrian Sherratt/The Guardian

  •  

Ofcom Investigates Pornhub Parent Aylo Over Age Checks

Pornhub age checks

Ofcom has opened an investigation into Aylo, the service provider of Pornhub, over its Pornhub age checks, examining whether the platform has met its legal obligations to prevent children from accessing pornographic content under the UK Online Safety Act.

The investigation focuses on a new age assurance process introduced by Pornhub in May 2026 for some users. The process relies on signals from Apple indicating that UK users attempting to access Pornhub may have completed Apple’s own age checks.

Under the Online Safety Act, responsibility for ensuring that age assurance is highly effective rests with the service provider, regardless of where in the process an age check takes place.

Ofcom Questions Pornhub’s Age Assurance Process

Ofcom said it is concerned that Aylo may not have carried out sufficient due diligence and testing before introducing the new process. The regulator is examining whether the system is sufficiently effective in preventing children from encountering pornography.

The investigation will assess whether Aylo complied with two key requirements under the Online Safety Act: using highly effective age assurance to prevent children from seeing pornography and completing a suitable and sufficient assessment of children’s access to the service.

Ofcom will also examine how Aylo implemented the process and whether the necessary due diligence was completed before deployment. The investigation will not determine how Apple operates its own age checks.

George Lusty, Ofcom’s Director of Enforcement, said online age checks are an important protection against children encountering inappropriate or harmful material and that technology companies are expected to ensure such systems are highly effective before deployment.

Ofcom Sets Out Investigation Process for Pornhub Age Checks

Ofcom said its investigation will begin with gathering and analysing evidence to determine whether a breach has occurred. If the regulator finds evidence of a compliance failure, it can issue a provisional decision to the company.

[caption id="attachment_114372" align="aligncenter" width="600"]Pornhub age checks Image Source: Ofcom[/caption]

Aylo would then have an opportunity to respond to Ofcom’s findings before a final decision is made.

If Ofcom determines that a company has broken the law, it can require the platform to take specific steps to comply with its obligations or address harm caused by the breach. The regulator can also impose fines of up to £18 million or 10% of qualifying worldwide revenue, whichever is greater.

Ofcom Expands Enforcement Against Intimate Image Abuse

The investigation comes alongside a separate Ofcom enforcement programme targeting the spread of illegal intimate images, including explicit AI-generated deepfakes.

Ofcom has said platforms should have automated hash matching technology in place by September 30 to detect and prevent the sharing of illegal intimate images. Platforms without hash matching must demonstrate that other systems and processes are equally effective at curbing the spread of non-consensual intimate images, or NCII.

Companies that fail to meet their legal duties could face fines of up to 10% of their global annual revenue.

Ofcom has partnered with SWGfL, which operates the StopNCII.org database and Revenge Porn Helpline, to share information and expertise on tackling intimate image abuse online.

The regulator is also seeking evidence from academics, survivor and victim support groups, and other stakeholders about how women’s and girls’ experiences online have changed.

Ofcom said the evidence will contribute to a report on industry progress in reducing online harms to women and girls. The regulator will also consider whether formal recommendations to the UK government are needed if industry action falls short.

The two enforcement efforts highlight Ofcom’s broader focus on requiring online services to put effective safeguards in place before harmful content or access risks materialise.

  •  

The Cyber Express Weekly Roundup: Hiscox’s SMB Warning, a Nintendo Switch Flaw, and a Record Deepfake Takedown

weekly roundup September 18 2026

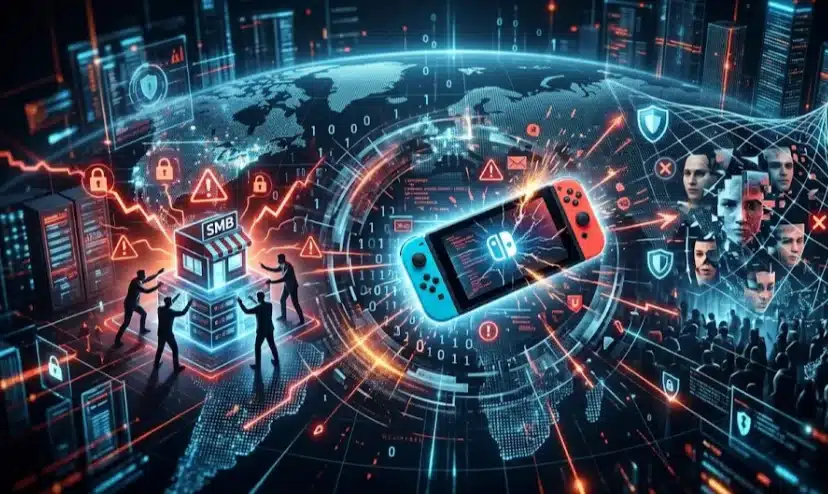
This weekly roundup covers a stark small-business cyberattack report out of the UK, a hardware flaw exposing Nintendo Switch owners to nearby attackers, the largest known seizure of AI deepfake porn websites, a candid conversation on AI's role in offensive security, new US legislation targeting elder fraud, and a fresh national threat-intelligence partnership in the UAE.  From consumer hardware to national policy, this week's developments show that exposure isn't limited to large enterprises or nation-state targets — small businesses, individual console owners, and everyday victims of fraud and non-consensual imagery are all squarely in scope, even as governments and industry move to close the gaps. 

The Cyber Express Weekly Roundup 

UK Small Businesses Face Higher Cyberattack Rates Than Global Peers, Hiscox Report Finds 

UK small firms are being hit by cyberattacks at a rate well above the global average, according to Hiscox's 10th annual Cyber Readiness Report. The survey of nearly 7,000 smaller businesses worldwide, including 1,000 in the UK, found that 38% of UK firms suffered a successful attack in the past year, compared with a 29% global average — the highest rate among all markets surveyed. Read more… 

Cyble Signs MOU with UAE Cyber Security Council to Boost National Threat Intelligence 

Cyble, an AI-native cybersecurity firm, has signed a Memorandum of Understanding with the UAE's Cyber Security Council to strengthen the country's national threat intelligence capabilities. Announced in Abu Dhabi in September 2026, the agreement centers on delivering advanced threat intelligence, early warning capabilities, and insights into emerging cyber risks facing government and critical infrastructure entities across the UAE. Read more… 

Nintendo Switch Flaw Let Nearby Attackers Run Code, Steal Data 

Nintendo has patched a flaw in the original Switch that let nearby attackers hijack its QR-code-based "Send to Smartphone" feature to run unauthorized code or steal data, including account information stored on the console. Tracked as CVE-2026-82079, the bug affected consoles on firmware older than version 23.0.0; the Switch 2 is unaffected. Read more… 

Manhattan D.A. Seizes 12 Deepfake Porn Websites in Largest Known Takedown of Its Kind 

The Manhattan District Attorney's Office has seized 12 websites allegedly used to create, sell, and distribute AI-generated deepfake pornography targeting roughly 1,200 real people without their consent. Announced by D.A. Alvin L. Bragg Jr., it's described as the largest known seizure of AI-generated celebrity deepfake websites to date, and the investigation is ongoing. Read more… 

Rahul Singh Choudhary on AI's Growing Role in Cryptanalysis and Offensive Security 

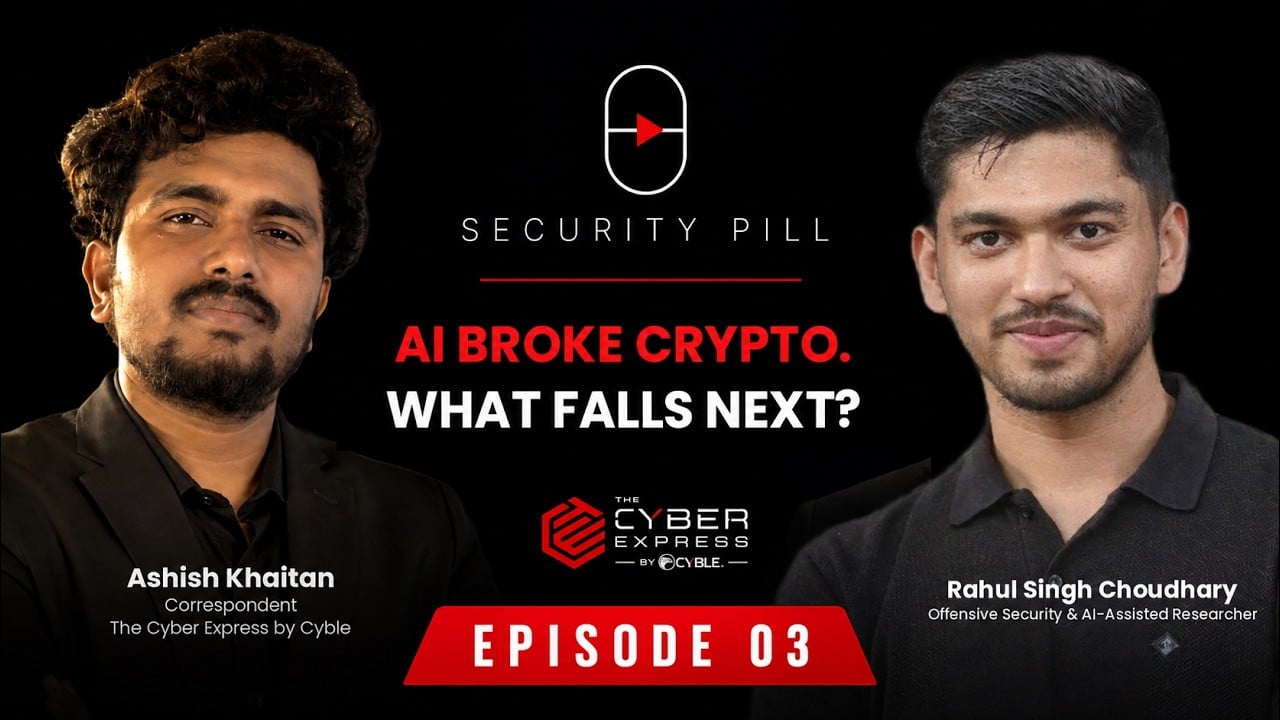
In the latest episode of Security Pill Season 2.0, The Cyber Express interviewed cybersecurity analyst Rahul Singh Choudhary about how AI is reshaping cryptanalysis, vulnerability research, and penetration testing. The conversation opens with a key question: has AI moved from merely assisting security research to actively participating in it — particularly around the cryptographic assumptions underpinning wallets, exchanges, and smart contracts? Read more… 

US House Passes GUARD Act to Boost Law Enforcement Fight Against Elder Fraud, Crypto Scams 

The U.S. House of Representatives has passed the bipartisan GUARD Act (H.R. 2978) on September 15, 2026, aimed at strengthening law enforcement's ability to combat elder financial fraud and cryptocurrency scams. Co-led by Representatives Josh Gottheimer, Zachary Nunn, and Scott Fitzgerald, the bill now heads to the Senate. Read more… 

Weekly Cybersecurity Takeaway 

This week's developments span the full spectrum of cyber risk — from small UK businesses absorbing a disproportionate share of attacks, to a hardware-level flaw putting console owners at physical-proximity risk, to AI tools being weaponized for non-consensual imagery at unprecedented scale.   Meanwhile, policy responses are accelerating on multiple fronts: US lawmakers are moving to arm local investigators against crypto-enabled elder fraud, and the UAE is deepening its national threat-intelligence posture through public-private partnership.  Taken together, the stories point to a widening gap between the speed of exploitation — whether by scammers, deepfake operators, or nearby attackers exploiting hardware — and the pace of institutional response, even as that response visibly picks up. 

💾

AI is already reshaping how crypto and blockchain systems get attacked — and defended. In this episode of Security Pill Season 2.0, we speak with Rahul Singh...
  •  

Manhattan D.A. Seizes 12 Deepfake Porn Websites Targeting 1,200 People

AI-generated deepfake

The Manhattan District Attorney’s Office has seized the domains of 12 websites allegedly used to create, sell and distribute AI-generated deepfake videos featuring approximately 1,200 real people without their consent. Authorities said the websites were used to publish and sell non-consensual intimate imagery created with artificial intelligence tools. The seizure, announced by Manhattan District Attorney Alvin L. Bragg Jr., involves what the office described as the largest known seizure of websites dedicated to AI-generated celebrity deepfakes to date. The investigation remains ongoing.

AI-Generated Deepfake Videos Target 1,200 People

According to the Manhattan District Attorney’s Office, individuals under investigation allegedly used AI image and video creation tools to transform existing photographs and videos of around 1,200 people into hyper-realistic images and videos depicting them engaging in sexual conduct. [caption id="attachment_114113" align="aligncenter" width="600"]AI-generated deepfake Image Source: https://manhattanda.org/[/caption] The websites were allegedly dedicated almost exclusively to deepfake pornography and explicitly promoted AI-generated content. The material was then distributed, published and sold through the websites. The approximately 1,200 people affected were overwhelmingly women, according to the D.A.’s Office. Many were public-facing individuals, including actors, politicians, athletes, musicians, social justice advocates and social media influencers. The office said the images and videos were created without the knowledge or consent of the people depicted.

12 Domains Seized Under Court Order

The Manhattan D.A.’s Office said the 12 domains were seized pursuant to a court order as part of the criminal investigation. Authorities said they will continue monitoring the websites to prevent the operations from returning under different domain names. [caption id="attachment_114112" align="aligncenter" width="600"]AI-generated deepfake Image Source: https://manhattanda.org/[/caption] The office is also urging people who believe they were affected to contact its Cyber Crime Bureau at 212-335-9600. The investigation comes as authorities examine websites allegedly built around the creation and distribution of non-consensual intimate imagery using artificial intelligence. District Attorney Bragg said the office would continue investigating the websites and similar operations. He also called on people affected by the websites to come forward.
Manhattan D.A. Expands Domain Seizures

The Cyber Crime Bureau has previously seized domains connected to other criminal investigations, according to the D.A.’s Office. Those cases included 12 domains from five online vendors accused of selling stolen credit and debit card information and personal identifying information. The office said those operations involved more than one million stolen cards belonging to people across the United States, including tens of thousands of New Yorkers. The bureau also seized the domain associated with Coin Dispute Network. The company was later indicted, along with its creators Michael Lauchlan and Gary Zaydman, over allegations that it stole from customers by falsely claiming it could trace and recover cryptocurrency for a fee. In the current investigation, Assistant District Attorneys Lotus Ho and Katherine Ellis are handling the case under the supervision of senior officials within the Cyber Crime Bureau and Investigation Division. The D.A.’s Office said its investigation into the 12 AI-generated deepfake websites and other potentially related operations is continuing.
  •  

CBI Searches 89 Locations Across 20 States in Digital Arrest Cases, Arrests Three

Digital Arrest, CBI, India, A darkened home desk with a laptop showing a fake police video call, illustrating a digital arrest scam in India.

India's Central Bureau of Investigation searched 89 locations across 20 states in three digital arrest fraud cases and arrested three people accused of moving the stolen money, the agency said.

The searches were conducted under Operation Chakra-VI, the agency's ongoing cybercrime enforcement programme. All three cases were transferred to the CBI from state police forces.

In a digital arrest, fraudsters posing as police officers, courts or central agencies contact a victim by phone or video call, allege involvement in a crime, and hold the person under sustained psychological coercion — often forbidding contact with family — while extracting transfers described as bail, verification deposits or asset audits.

The three cases together account for about ₹42.4 crore (approx. US$4.49 million) in losses, an official press release stated. One, linked to the Birla Institute of Technology and Science, Pilani, involved a victim kept under digital arrest for three months and defrauded of ₹7.67 crore by callers impersonating police officers. The release does not specify the victim's role at the institution. A second case in Gujarat also ran three months and cost the victim ₹19.24 crore, again to scammers posing as police. The third, in Karnataka, involved a month of coercion and ₹15.45 crore.

Those durations are the notable detail. Where most online fraud is transactional, these cases show victims held in a controlled state for weeks or months, which is what allows losses to climb into crores from a single target.

The CBI said the searches were planned on the basis of financial and technical analysis, including examination of bank accounts and online account access records, and were carried out simultaneously to prevent destruction of evidence. Investigators seized banking documents, account records and digital devices, which the agency said are now undergoing forensic examination to map the financial and technological infrastructure supporting syndicates operating across state lines.

Also read: CBI Files Charges Against 13 in Digital Arrest Fraud Case Linked to Myanmar Cyber Slave Compounds

The three people arrested are described as beneficiaries in the laundering chain rather than the callers. Akash, a resident of Haryana, allegedly received ₹1.95 crore into an account he opened himself and pushed the funds onward to other accounts the same day. Raja Karmakar of Kolkata is accused of receiving ₹1.5 crore into his firm's account. Jyoti Rani allegedly received part of the proceeds, withdrew some in cash and transferred the rest onward. The agency said efforts continue to trace the remaining accused.

On Dec. 1, 2025, a Supreme Court bench of Chief Justice Surya Kant and Justice Joymalya Bagchi ordered a pan-India CBI investigation into digital arrest scams, specifically directing scrutiny of mule accounts and alleged collusion by bank officials, and requiring several states to grant the agency consent under the Delhi Special Police Establishment Act. In interim directions issued Aug. 5, 2026, the court told the Reserve Bank of India to publish a standard operating procedure for banks handling mule accounts, pressed states to notify cyber crime coordination centres, and ordered an inter-departmental committee to examine a shared-liability and victim compensation framework.

Home ministry figures cited before the court show digital arrest complaints falling from 123,672 in 2024 to 58,249 in 2025 and 16,377 through June 30, 2026, with ₹18.05 crore restored across 36,290 cases. The trend is fewer complaints but heavier individual losses.

  •  

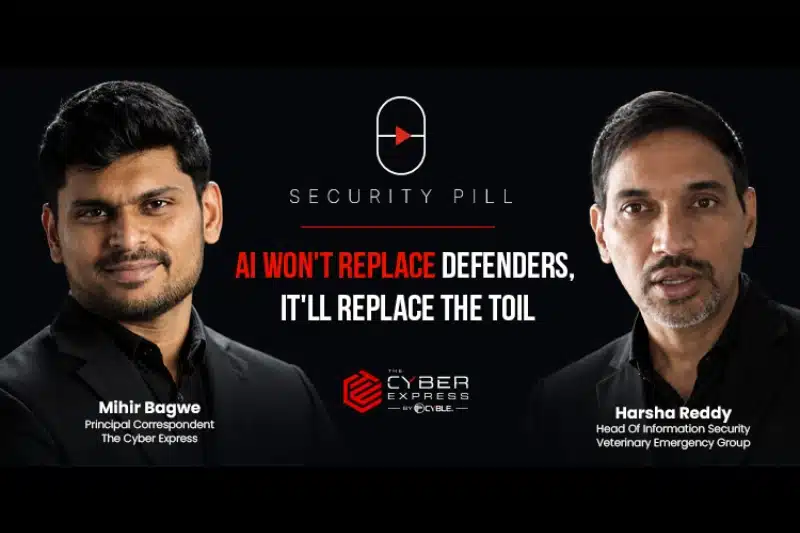
AI Won’t Replace Cybersecurity Jobs, It’ll Replace the Toil – Harsha Reddy Explains What’s Next

AI, Cybersecurity, Harsha Reddy

As enterprises race to bolt AI onto every business process, security leaders are being forced to answer a harder question than "should we adopt it" — it's "who's accountable when it goes wrong." To unpack this, The Cyber Express sat down with Harsha Reddy, Head of Information Security at Veterinary Emergency Group (VEG).

With nearly two decades in security leadership — including senior roles at Lixil and American Standard before joining VEG — Harsha brings a practitioner's view of where AI is genuinely changing the CISO's job, and where it's mostly just hype and shadow adoption.

Watch the Full Interview:

Harsha Reddy Explains Why AI Will Replace Tasks, Not Defenders

Harsha pushes back on the narrative that AI will hollow out security teams, pointing to Gartner research showing that while most fields are projected to lose jobs to AI, cybersecurity is expected to gain them. In his view, the technology is mainly absorbing the "toil" — log review, alert triage, evidence gathering — that keeps analysts from actually defending.

Also listen to S1 Episode: Awareness and Education at Young Age is the Answer to Cybersecurity Skill Gap

“It's the analyst who refuses to use AI that will get replaced by an analyst who uses it,” he says.

On adoption, Reddy points to a 2024 Microsoft-LinkedIn survey in which most executives called AI critical to their business, yet a majority had no formal plan and most had employees already bringing in their own tools. That gap, he argues, is why so many organizations are now dealing with AI-related data leaks. "Many organizations started onboarding AI like software when they should be onboarding it like staff." His fix isn't more restrictions — blocking AI just pushes it into the shadows — but guardrails, an internal AI enablement committee, and measuring actual business value instead of token consumption.

The conversation also digs into deepfake-driven fraud, why training employees to spot deepfakes is “a losing bet” at machine speed, and how he decides when to greenlight a new AI tool versus telling a business unit “not yet.”

The conversation closes with our newly introduced rapid-fire round "Express Shots" — Claude vs. ChatGPT, passkeys vs. passwords, and Reddy's prediction for the biggest cybersecurity threat of 2030.

💾

As enterprises race to bolt AI onto every business process, security leaders are being forced to answer a harder question than "should we adopt it" — it's "who's accountable when it goes wrong."
  •  
❌