❌

Reading view

We need to stop disinformation in UK political adverts. Here’s a chance to do so | Letter

Alex Tait on a proposed amendment to the representation of the people bill, and Dr Joseph Mullen on Russian interference in the Brexit referendum

Andy Burnham’s comments about Russian interference in Brexit (Report, 11 October) and the warning by the MI5 chief, Ken McCallum, against exaggerating its impact (Report, 13 October) risk overlooking another serious threat to electoral integrity: disinformation from our own political parties and campaigners.

Foreign interference deserves scrutiny, but misleading factual claims in electoral advertising are unregulated, unlike in commercial advertising. We have four sets of rules to ensure an advert for a packet of sausages is accurate, but none for the most important advertising of all – ads that influence how we vote.

Continue reading...

© Photograph: Tuomas A Lehtinen/Getty Images

© Photograph: Tuomas A Lehtinen/Getty Images

© Photograph: Tuomas A Lehtinen/Getty Images

  •  

The hill I will die on: Cinemas have been getting away with lies. Films should begin on time | Jeffrey Ingold

If cinemas must run 20 minutes of adverts before a feature, they could at least be honest about it. Or, I have a better solution …

Do you remember the last time you were lied to? I certainly do. I was tricked by the North Finchley Vue, which sold me and my boyfriend tickets to a 7.15pm showing of The Odyssey. Guess what was playing at 7.15pm? A car advert. Ten minutes later, it was a trailer for the horror film Werwulf. Then there was an advert for Vue – as if I wasn’t already there. The film was half an hour late to its own showing when it finally started at 7.45pm.

I am sick and tired of cinemas getting away with such treachery. I don’t want to follow in the footsteps of my friend, who knows that the ads at her local run for 22 minutes so slinks in at just the right time. I shouldn’t have to do mental maths because I am being lied to by cinemas. We are all the victims of their predatory time-wasting system.

Jeffrey Ingold is a freelance journalist covering LGBTQ+ issues, music and culture

Continue reading...

© Composite: Guardian Design/Getty Images

© Composite: Guardian Design/Getty Images

© Composite: Guardian Design/Getty Images

  •  

Meta Withdraws $25 Million from Its Midterms Push

The company outlined a $65 million budget last year when it embarked on an effort to elect state politicians friendly to the A.I. industry.

© Gabriela Bhaskar/The New York Times

Meta’s annual conference last month in Menlo Park, Calif. The company received $22 million back from its American Technology Excellence Project and $3 million from a California advocacy group it funded.
  •  

First-Ever Public Confirmation of 'Zero-Click' Spyware Delivered Via Targeted Ads

Citizen Lab says it has documented the first publicly confirmed case of zero-click mercenary spyware being delivered through targeted online ads, a technique it calls "AdFection." "There has been a lot of buzz that online ads can be used to identify and automatically hack targets with pinpoint precision, but now for the first time, we have concrete technical evidence showing this process in action," said Bill Marczak, a researcher at Citizen Lab. The Guardian reports: Citizen Lab, a digital investigations research unit at the University of Toronto, said it believed dozens of devices at the Qatari broadcaster Al Jazeera had been compromised by spyware delivered through ads run by Discover-Tech, which describes itself as a specialised digital advertising agency. According to Citizen Lab, Discover-Tech operates a software platform called Controlium that allows its clients to "mass-profile and deanonymize" internet users then covertly hack targets with third-party spyware. Unlike infections that rely on people interacting with links or files, the spyware requires no interaction from the victim to be installed, making it a new delivery technique, Citizen Lab says. The infections happen without a user's knowledge, and in a matter of seconds, according to Citizen Lab. "[The online advertising] ecosystem is being weaponized at a massive scale to profile millions of users, then silently infect targets with zero-click mercenary spyware," the report says. According to the report, Controlium is able to harvest a user's identity and IP address when the user is shown a seemingly benign custom-created ad -- for example, for a digital game or a telecoms service. If the user has been selected as a target for hacking, a mercenary spyware firm can then send a malicious code containing spyware to their device, the researchers say. They say that millions of users worldwide have been served ads by Discover-Tech since 2024, including in Yemen, Brazil, Mexico and Czechia. [...] The full extent of the targeting allegedly enabled by Discover-Tech is unknown. Citizen Lab's findings join mounting evidence that the opaque arrangements underpinning the world of online advertising can be leveraged for surveillance.

Read more of this story at Slashdot.

  •  

Online ads weaponised to deliver ‘zero-click’ spyware, researchers say

Discover-Tech’s Controlium software lets clients mass-profile internet users then covertly hack targets, say researchers at University of Toronto

An Israeli advertising agency has been serving millions of online adverts that allow “zero-click” spyware to be used against targets, researchers at a Canadian university have said.

Citizen Lab, a digital investigations research unit at the University of Toronto, said it believed dozens of devices at the Qatari broadcaster Al Jazeera had been compromised by spyware delivered through ads run by Discover-Tech, which describes itself as a specialised digital advertising agency.

Continue reading...

© Photograph: Sergio Azenha/Alamy

© Photograph: Sergio Azenha/Alamy

© Photograph: Sergio Azenha/Alamy

  •  

Lost generation: the AI threat to Britain’s next great directors

Commercials once launched careers from Ridley Scott to Guy Ritchie, now automated production is cutting costs – and the chance to learn by doing

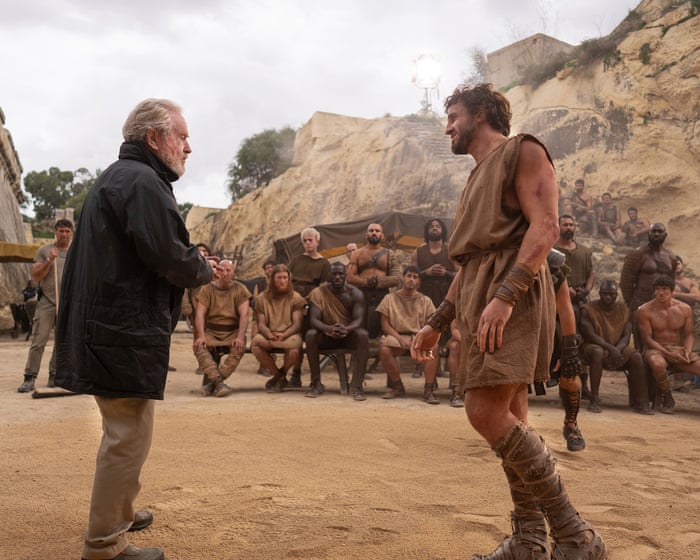
When Ridley Scott was awarded the UK’s highest accolade for a glittering career directing films from Alien and Blade Runner to Gladiator and The Martian, he reminded those attending the Bafta event eight years ago that making commercials had been his “film school”.

The advertising industry has long been a breeding ground for British film and TV talent who have gone on to make the jump to Hollywood productions, including Guy Ritchie, who started out making music videos and commercials, and Paddington in Peru director Dougal Wilson, whose credits include a number of John Lewis’s famous Christmas ads.

Continue reading...

© Photograph: Aidan Monaghan/AP

© Photograph: Aidan Monaghan/AP

© Photograph: Aidan Monaghan/AP

  •  

We Asked Starbucks Why Their 'Sugar-Free' Drinks Have Sugar...

...and Now We're Just More Confused. "A federal lawsuit filed Friday alleges that Starbucks is misleading consumers with a line of "sugar-free" drinks that actually contain a significant amount of sugar. The company denies the allegations, but a quick visit to the Starbucks website reveals that some drinks labeled as sugar-free also have nutrition labels that explain the beverages have as much as 21 grams of sugar."

Related from 2024: 'Boneless' chicken wings can have bones, the Ohio Supreme Court says Previously on the blue: Burger King must defend its Whopper size in court. Other fast food chains may follow
  •  

O2 signs record £200m deal to keep London venue’s naming rights

Exclusive: 10-year sponsorship extension at a 50% premium on last agreement crowns bonanza year for live venue

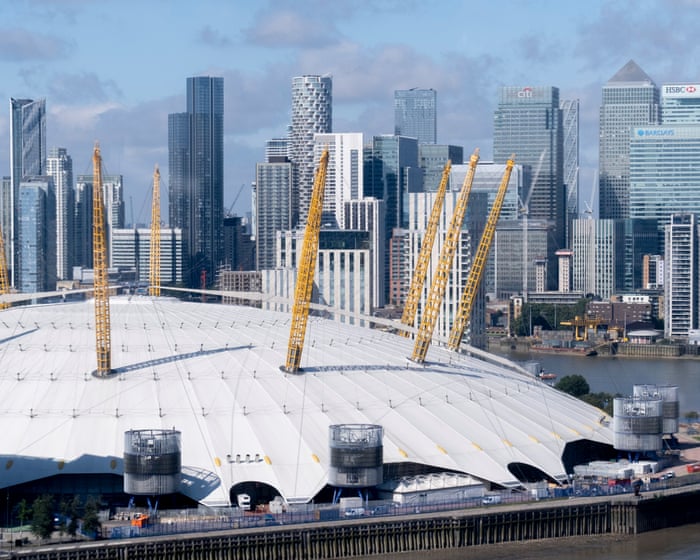
O2 has struck a record deal thought to be in the region of £200m to retain the naming rights to the London venue the O2 in the largest renewal of its kind in UK history.

The 10-year agreement will extend O2’s relationship until at least 2038. It cements the sponsorship as the second longest-running UK stadium naming rights deal after Arsenal’s partnership for the football club’s London ground,

Continue reading...

© Photograph: Richard Baker/In Pictures/Getty Images

© Photograph: Richard Baker/In Pictures/Getty Images

© Photograph: Richard Baker/In Pictures/Getty Images

  •  

StreamRat Android malware spreads through Meta and TikTok ads

A malicious advertising campaign promoting a fake free TV-streaming service reached roughly 570,000 Meta users.

The researchers who discovered the campaign found that its streaming-themed ads were aimed at Spanish-speaking users, with most observed victims located in Spain. One Meta campaign ran from June 11 through July 3, 2026, and the same banners were also used to distribute the malware through TikTok.

The available data shows the ads’ reach, not the number of downloads or infections, but it demonstrates how quickly paid advertising can put a scam in front of a very large audience.

The ads promoted an Android banking Trojan and infostealer called StreamRat. It can monitor what’s on screen, capture information typed into apps, show convincing fake screens to steal usernames and passwords, and allow attackers to control the device remotely.

We often warn people not to click suspicious links in unexpected texts or emails. But malicious advertising is harder to recognize because it appears in the same feeds where people expect to find promotions, videos, and recommendations.

This campaign is a perfect demonstration of why “after-the-fact” ad checks are inadequate when it comes to protecting social media users. Attackers used familiar social media advertising and carefully tailored instructions to turn casual interest in free entertainment into a risky app installation.

How the attack worked

The ad led victims to a website posing as a streaming platform. The site checked whether a visitor was using Android. Non-Android visitors were simply prevented from downloading anything, while Android users were shown an app download option. This is a common way for scammers to concentrate their efforts on devices their malware can infect.

The site also identified whether someone had arrived through Instagram, TikTok, Facebook, or a regular browser. It then displayed instructions suited to that situation, including steps to allow the browser to install apps from “unknown sources.” In other words, this was not a generic malicious download page: It was designed to coach people through the security warnings that would normally make them stop and think.

StreamRat is an Android banking Trojan and infostealer. It can monitor what’s on screen, capture information typed into apps, show convincing fake screens to collect usernames and passwords, and enable attackers to operate the device remotely. The researchers also found options to cover the screen with a black page or fake Android update screen. These can distract victims while criminals interact with the phone behind the scenes.

How to stay safe

While this campaign targeted Spanish-speaking people, primarily in Spain, the following guidelines can help anyone avoid similar attacks.

  • Avoid installing Android apps from ads, direct-download websites, social media messages, sponsored search results, or links sent by strangers.
  • Download apps through Google Play whenever possible, and check the developer’s name, reviews, and app history rather than relying on an ad.
  • Before enabling installation from “unknown sources,” read our guide, Sideloading on Android: What it is, why it’s risky, and how to do it more safely.
  • Be very cautious when an app asks for Accessibility access, screen-sharing permission, Device Admin privileges, or permission to become the default launcher. Permissions that don’t line up with the intended use of the app are very suspicious.
  • Use an up-to-date, real-time anti-malware solution on all your devices.

What to do if you installed a suspicious app

If you installed a suspicious APK and granted it Accessibility access, disconnect the phone from Wi-Fi and mobile data. If possible, revoke the app’s Accessibility access and remove it. Use another device to change relevant passwords and contact your bank if you used banking apps on the infected phone. A factory reset may be necessary if you cannot confidently remove the infection.

Malwarebytes for Android detects the components of StreamRat as Android/Trojan.Agent.ACRAEEF8A36H36, Android/Trojan.Agent.ACR02DB0614H7, and Android/Trojan.Dropper.ACR9B7ECE83D1.


Scammers know more about you than you think. 

Malwarebytes Mobile Security protects you from phishing, scam texts, malicious sites, and more. With real-time AI-powered Scam Guard built right in. 

Download for iOS → Download for Android → 

  •  

Why the Courts Are Hesitant to Punish Tech Giants Like Meta and Google

After finding antitrust violations, federal courts have been reluctant to impose harsh sanctions. They fear meddling in markets where technology is racing ahead.

© Kelsey McClellan for The New York Times

Creating effective remedies is difficult for the courts, particularly because of the rapid pace of change in the tech industry.
  •  

FTC and 22 States Sue Amazon Over Advertising Practices

Regulators say the e-commerce giant forced more than a million advertisers to pay more than they should have. The company denies the claims.

© Vincent Alban/The New York Times

The Federal Trade Commission and the states said Amazon misled brands and sellers into paying more for ads; the company is denying the accusations.
  •  
❌