❌

Reading view

Hackers Hijack D-Link, Ubiquiti Devices To Resell Your Stolen Bandwidth

An anonymous reader quotes a report from BleepingComputer: A proxyjacking campaign has impacted devices in 34 countries, monetizing victims' internet connections through a commercial residential proxy network. The operator installed Pawns.app, a legitimate bandwidth-sharing application that lets users earn money by sharing their internet connections, on devices without the owners' consent. Pawns.app account holders are rewarded for allowing traffic from other users to flow through their network, provided it runs on trusted, non-blocking IP addresses. By installing the app on multiple systems, the attacker likely accumulated larger payouts. Threat intelligence company GreyNoise discovered the campaign while investigating suspicious activity at an unnamed organization, and identified at least 143 compromised devices worldwide. According to researchers, the attacker exploited known vulnerabilities in D-Link ShareCenter NAS (CVE-2024-3272 and CVE-2024-3273), Ubiquiti UniFi Video NVR (CVE-2021-44228), and SAP NetWeaver Visual Composer (CVE-2025-31324) to install the Pawns.app software. Hikvision and Dahua DVR/NVR devices were also targeted, though the specific vulnerabilities exploited were not identified. In some cases, the report says the attackers configured SSH key authentication to maintain backup access to the compromised systems.

Read more of this story at Slashdot.

  •  

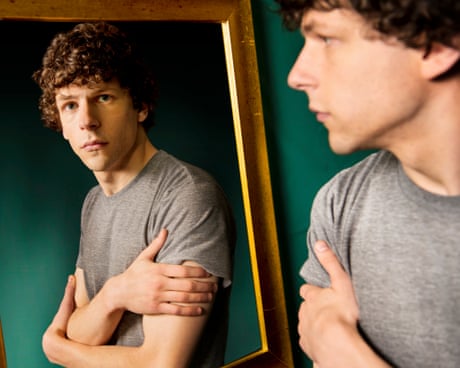
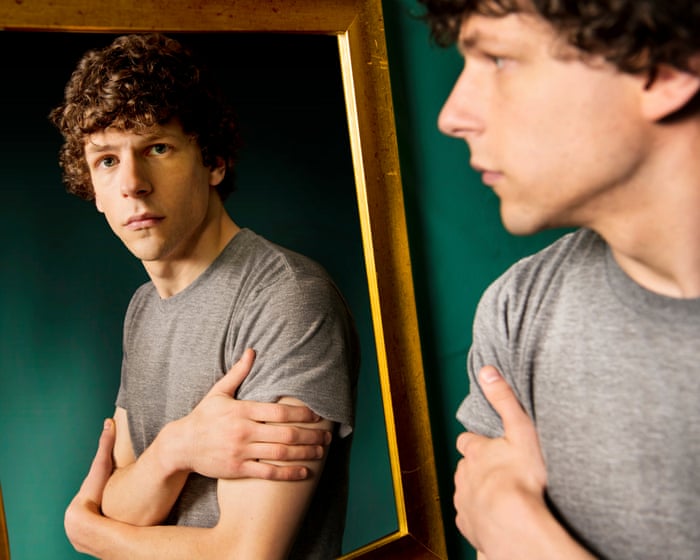
Your full attention: Jesse Eisenberg’s 10 best film performances – ranked!

As his new movie The Debut closes the London film festival, we count down the best of the actor’s shy, sly and sometimes hairy outings

A doppelganger role can be a trap for an actor: either the two roles are not sufficiently distinct, or they are too hammily different, and either way the result can look like a film school graduation project. But Jesse Eisenberg gives a stylish split-personality turn in Richard Ayoade’s adaptation of the Dostoevsky novella. He plays Simon, a nerdily shy and self-effacing computer programmer in a grim futureworld, ignored by his employers and by co-worker Hannah (Mia Wasikowska), with whom he is hopelessly in love. But then his carbon copy, James, arrives, also of course played by Eisenberg. James is a confident alpha-achiever who impresses his bosses and entrances Hannah – to Simon’s gibbering despair.

Continue reading...

© Photograph: Linda Nylind/The Guardian

© Photograph: Linda Nylind/The Guardian

© Photograph: Linda Nylind/The Guardian

  •  

The Social Reckoning isn’t as angry or as potent as a Facebook drama should be

Aaron Sorkin’s attempt to return to the success of The Social Network is a strangely dated and incomplete look at a world that needs a sharper eye

In retrospect, David Fincher’s 2010 film The Social Network was a landmark for a quiet, even counterintuitive reason. Before the film was released, some questioned whether Aaron Sorkin, a writer not exactly known for his mastery of, nevermind obsession with, the technical sphere, was the right man to tell the origin story of Facebook. And while Sorkin may well have converted Mark Zuckerberg into terms he could better understand – namely, a motormouthed wiseass who deep down wants to impress a smart, serious-minded girl – he and Fincher also made one of the first internet-centric movies to treat online life as a natural extension of IRL dynamics, rather than the otherworldly tech portal seen in so many 90s internet movies.

Granted, that’s the whole deal with Facebook: its viral spread of social networking, something so simple and addictive that aunts, grandpas and coworkers everywhere could understand it. Yet understanding its simultaneous extension and distortion of the real world wasn’t a given; four years later, for example, 2014’s Men, Women and Children was widely derided for taking an alarmist approach to the internet as a haven for adults seeking an affair, teenagers nursing porn addictions and fame-hungry strivers of all ages. The Social Network, on the other hand, is remarkably nonjudgmental about the basic mechanics of Facebook, rooting its nascent flaws in the human weaknesses that birthed it. In retrospect, the movie only feels outdated to the extent that it underestimates Zuckerberg’s grasping for power and the potential for grim carelessness that his online kingdom was built on.

Continue reading...

© Photograph: Leah Gallo/Sony Pictures/AP

© Photograph: Leah Gallo/Sony Pictures/AP

© Photograph: Leah Gallo/Sony Pictures/AP

  •  

EU Cybersecurity Response Hampered by Critical Information Gaps

EU cybersecurity incidents

The European Union’s ability to detect and respond to EU cybersecurity incidents faces significant gaps, particularly in information-sharing and coordination between national and EU-level bodies, according to a new report by the European Court of Auditors (ECA). The auditors said the EU has made progress in developing a cybersecurity cooperation framework, but several measures needed to support an effective response to significant and large-scale incidents are still incomplete. Cybersecurity incidents can disrupt public services, businesses, critical infrastructure and the EU’s internal market. While member states remain primarily responsible for responding to such incidents, the EU has a role when attacks cause major disruption, significant financial losses or substantial harm, or when incidents affect several countries and exceed the response capacity of a single member state.

EU Cybersecurity Incidents Face Information-Sharing Gaps

The ECA identified insufficient information exchange as a major weakness in the EU’s cybersecurity response system. The Cyber Blueprint, adopted in 2025, largely clarifies roles and responsibilities for managing major cybersecurity crises. However, the cooperation between two key EU cyber networks has not yet been formally defined. The auditors said this affects cooperation between the CSIRTs network, which brings together national teams responsible for handling cyber incidents, and EU-CyCLONe, which supports cooperation during EU-level cyber crises. Information-sharing is also affected by differences in national security laws and the ongoing implementation of updated EU cybersecurity rules, including the NIS 2 Directive. According to the auditors, these factors can make it harder for EU networks to identify threats early and coordinate an effective response. “The EU has made progress in building a cybersecurity cooperation framework, but it is not yet working as effectively as it should,” said George-Marius Hyzler, the ECA Member responsible for the audit. “When a serious cyber incident occurs, timely and actionable information is essential. Without it, networks and mechanisms lose much of their added value.”

European Cybersecurity Alert System Still Delayed

The audit also found that the European Cybersecurity Alert System was not operational at the time of the assessment. Two hubs examined by the auditors, ATHENA and ENSOC, had not started operating because of procurement delays. The system also lacked several elements needed for operation, including cooperation agreements, a common classification system and technical standards. The findings come as the EU continues to invest in cybersecurity. Under the 2021-2027 EU budget, €1.4 billion has been allocated to cybersecurity through the Digital Europe Programme, the EU’s main source of cybersecurity funding.

Overlap Among EU Cybersecurity Bodies

The ECA also identified overlapping responsibilities among some EU bodies involved in monitoring cybersecurity threats. The European Commission’s cyber situation centre, established in 2022 and largely supported by external providers, carries out work that the auditors said partly duplicates existing capabilities at the European Union Agency for Cybersecurity (ENISA). These capabilities include monitoring threats and developing cybersecurity situational awareness. The auditors called for better coordination to reduce duplication and strengthen the overall effectiveness of the EU’s cybersecurity framework.

Funding Checks Raise Security Concerns

The report also highlighted weaknesses in checks on some organisations receiving EU cybersecurity funding. These checks are intended to reduce risks linked to intrusion or influence by non-EU states and prevent sensitive security information from being shared with non-EU authorities. However, while grant beneficiaries are responsible for assessing the ownership and control of third parties receiving financial support, the European Cybersecurity Competence Centre does not verify those assessments. The ECA warned that this could expose sensitive infrastructure, operational data and security-critical technologies to security risks. The audit covered the period from 2022 to 2025 and assessed whether EU actions effectively supported the detection of and response to significant and large-scale cybersecurity incidents. Audit missions were conducted in Ireland, Greece and Italy.
  •  

Free streaming boxes may be routing criminal traffic through your home

“Free” movies and TV could cost you your privacy, bandwidth, and control of your home network.

We’ve warned about illegal streaming and modded Amazon Fire TV Sticks in the past. Now, researchers have found that certain SuperBox devices and apps could quietly enroll a household connection into a proxy network, allowing third parties to route traffic through it.

An earlier report identified CyberFlix TV, available through SuperBox’s custom app store, as containing Popanet proxy functionality that registers the device with a server controlled by the proxy operator.

Law enforcement agencies have warned that “foreign entities” are using residential proxies to conceal their identities and make their activity appear to come from someone else’s home network.

The FBI defines a residential proxy as follows:

“A residential proxy is an intermediary server between individuals and websites they visit to make their connections appear to originate elsewhere. Legitimate IP addresses assigned by an Internet Service Provider (ISP) to consumers’ Internet of Things (IoT) devices, such as TV streaming devices, digital picture frames, smartphones, tablets, and routers are used to route traffic. Once an internet-connected device is compromised, the device’s IP address can be used by threat actors to mask their online illegal activity, making the consumer appear responsible.”

Residential proxy networks rent out ordinary home IP addresses to customers. That makes their traffic appear as if it originates from a legitimate consumer connection rather than a data center, helping cybercriminals evade IP-based fraud controls and reputation systems.

Besides affecting connectivity, this can mean that a household’s public IP address becomes associated with activity it did not initiate, ranging from credential stuffing and account abuse to attempts to bypass enterprise security controls.

Plume’s more recent research warns that these proxy networks can also function as malware-delivery platforms. In other words, attackers may not only use a compromised streaming box as an exit node. They may use the proxy connection to reach the box itself and install additional malicious software.

The reported SuperBox configuration is especially troubling because it disables or weakens multiple Android safeguards. Researchers found exposed Android Debug Bridge (ADB) access, root-level privileges without authentication, and the removal of protections that would normally restrict untrusted app installation or prompt users to approve risky actions.

Many people assume that placing a streaming device behind a home router prevents outside access. Normally, network address translation and a firewall do make unsolicited inbound connections more difficult. But proxy-enabled devices can maintain an encrypted outbound connection to a remote server, creating a channel that the home router treats as legitimate traffic initiated from inside the network.

How to stay safe

The safest option is not to connect devices or install apps that promise unauthorized access to free movies and TV. You could be bringing a proverbial Trojan horse into your home.

If you own a SuperBox device or have installed CyberFlix TV, disconnect the device from your network. A factory reset may not be enough to make it safe to use again, so you should replace it.

When a device’s business model depends on monetizing your connection, its security choices can put your IP address, bandwidth, privacy, and local network at risk.

Network segmentation can reduce exposure for ordinary Internet of Things (IoT) devices, but it is not a complete answer here. A product that intentionally establishes a persistent proxy channel and offers weak device-level protection should not be trusted on a household network, even on a separate guest network.


From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

  •  
❌