❌

Reading view

Meta glasses caught recording conversations without wake phrase

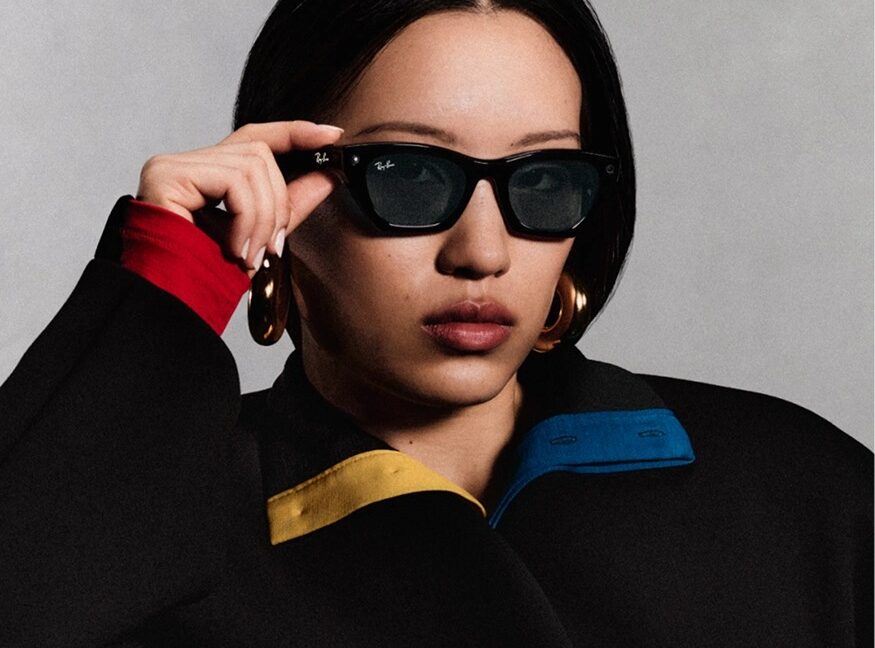
Meta says it has resolved an issue after some Ray-Ban Meta owners reported that their glasses recorded conversations without the “Hey Meta” wake phrase.

Users reported finding recordings and transcripts of conversations they did not knowingly save. Recording without anyone realizing raises privacy concerns for both the wearer and the people around them.

The complaints surfaced on Reddit, where one owner described unexpected recordings occurring with three pairs of glasses. The owner said the behavior started after a firmware update and occurred even with Respond without Hey Meta disabled. They also reported that the glasses’ internal notification light sometimes activated during normal conversation. Other commenters described similar unexplained activations.

As Android Authority reports, Meta says the problem has been fixed:

“This issue has been resolved. People can manage, review and delete voice logs of their interactions with Meta AI via settings at any time.”

What’s missing is a public explanation of what caused it, how many people were affected, and what happened to the audio captured.

This isn’t the first time we’ve reported on privacy concerns involving smart glasses. In June, we covered unreleased facial-recognition code found in Meta’s companion app. The code was not active, but the reporting raised concerns about how wearable cameras could eventually move from capturing people to identifying them without their knowledge.

What owners can do

According to the Reddit owner, Meta Support recommended disabling microphone and camera permissions, turning off Wear Detection, deleting voice history, and disabling automatic updates. Those steps would limit much of the gadget’s core functionality without explaining what went wrong.

Until Meta provides a fuller explanation, here are a few precautions that make sense if you wish to keep using your smart glasses:

  • Review your voice history. Look for interactions you do not recognize and delete unwanted recordings or transcripts. Meta says users can manage these logs through Settings.
  • Check your voice-activation settings. The owner reporting the issue said Respond without Hey Meta was already disabled, so do not treat that setting alone as a guarantee against unintended activation.
  • Keep the glasses and companion app updated. Although the user associated the behavior with an update, that is not a good reason to permanently abandon updates that may contain security and privacy fixes.
  • Always ask before recording other people. Their privacy matters even when your glasses are working exactly as intended.

Meta still owes users an explanation of what went wrong and what it has done to ensure it won’t happen again.


Browse like no one’s watching. 

Malwarebytes Privacy VPN encrypts your connection and never logs what you do, so the next story you read doesn’t have to feel personal. Try it free → 
  •  

Bug turns one of the biggest fears about Ray-Ban Meta smart glasses into reality

Some Ray-Ban Meta smart glasses were recording people’s conversations without the wearer knowing. The recordings occurred without users saying the prompt phrase (“Hey, Meta”), in a bug that Meta says has been fixed.

This week, some users reported online that their Ray-Ban Metas were recording without their consent. A person going by Kindly-Audience-137 on Reddit, for example, said this happened to them across three Meta Ray-Bans and that they had the “Respond without Hey Meta” setting turned off. The person said the Meta AI app “saves audio recordings and text transcripts of these conversations in my conversation history.”

“I believe this deserves a serious technical investigation. Customers should not have to wonder whether their private conversations are being captured when they have not intentionally activated their glasses’ AI assistant,” the Reddit user said.

Read full article

Comments

© Meta

  •  

Some cheap smart glasses are a security disaster

Apart from the privacy concerns around smart glasses, researchers have found that some cheap brands come with barely any security at all.

ABC Australia reports that researchers from NSB Cyber and Abstract Shield tested two inexpensive pairs, costing A$60 and A$110 (around US$42 and US$78), and found more than a dozen flaws across the smart glasses themselves, their app, and an associated website.

The main problem they uncovered was insecure Bluetooth pairing: If the glasses were powered on and not connected to their owner’s phone, an attacker could connect first, with no password or meaningful pairing confirmation.

After connecting, an attacker could reportedly control the glasses to capture photos or recordings, copy existing media, and intercept data moving between the glasses and the phone. An attacker could also make another device appear to be the victim’s glasses, allowing it to connect to the owner’s mobile app.

The testing also found that a Bluetooth-visible device identifier could allegedly be used with a weakness in the app’s website to retrieve a user’s email address and date of birth.

The research uncovered another privacy issue. ABC reports that voice or text submitted to the built-in AI, along with images sent to it, was first transmitted to a server in Shenzhen and could be forwarded elsewhere, depending on the function. The tests did not establish how the data was subsequently used.

The server locations, combined with some of the AI’s answers to specific questions, led researchers to conclude that the chatbot companion relied at least in part on Chinese sovereign AI models. Professor Kimberlee Weatherall, a technology regulation expert involved in the testing, said the failure to identify China in the privacy policy appeared to violate the Australian Privacy Principles,

The timing of the testing is also relevant because Australia’s smart-device security standards apply to most consumer smart devices manufactured on or after March 4, 2026. They require, among other measures, no universal default passwords, a way to report vulnerabilities, and information about the minimum security-update period. Devices made before that date are outside the requirements.

Experts quoted by ABC said the devices violated Australia’s privacy laws and were also likely to breach several sections of the Cyber Security Act. However, whether the new smart-device standards apply would depend partly on when the glasses were manufactured, and the rules have not yet been tested in a known enforcement action.

Professor Weatherall said:

“The rules say that the password must be unique. It doesn’t even seem like they were applying a password, which might mean that their standards are so low they don’t even technically breach that rule, which I find amazing.”

What to do

We’re not fans of smart glasses, expensive or cheap. But if you own a pair:

  • Avoid pairing or using inexpensive camera glasses that lack a clear physical pairing step, account authentication, a published security-contact process, and a stated update-support period.
  • Stop using their AI or cloud features for sensitive material, remove unnecessary permissions from the companion app, check for firmware and app updates, and consider returning the product if the vendor cannot document a fix.
  • Ask permission before recording people, and check your local laws to understand what is and isn’t allowed.

From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

  •  
❌