❌

Normal view

A sextortion conspiracy killed his son (Lock and Code S07E21)

19 October 2026 at 08:10

This week on the Lock and Code podcast…

At just 17 years old, Jordan DeMay was murdered by strangers online.

That’s how Jordan’s father, John DeMay, described what happened to his son four years ago. At home in Michigan, Jordan was readying for a weekend trip when he received a friend request on Instagram. The invite was sent by a user named “dani.robertts” whose profile showed an attractive young woman. After accepting the request, Jordan and the account chatted about nothing in particular—teenage matters, getting to know one another—before “dani” became flirtatious, eventually sending Jordan what she claimed was a nude photograph of herself.

Jordan responded in kind with an explicit photograph of himself.

But here, a trap was revealed.

“Dani Robertts” was not a young, friendly, interested woman. Dani Robertts was several men, sending messages from thousands of miles away in Lagos, Nigeria, who had followed a script to pressure young men into handing over their money. This was not the first time these men had run this scam. But with a great deal of investigative work, it hopefully has become the last.

What happened to Jordan can happen to anyone—and it has happened to far too many young men and women today. It is a type of attack commonly referred to as “sextortion.”

Today, on the Lock and Code podcast with host David Ruiz, we speak with John DeMay about his son Jordan, his family’s relationship with social media, and what parents should know.

Tune in today to listen to the full conversation.

Show notes and credits:

Intro Music: “Spellbound” by Kevin MacLeod (incompetech.com)
Licensed under Creative Commons: By Attribution 4.0 License
http://creativecommons.org/licenses/by/4.0/
Outro Music: “Good God” by Wowa (unminus.com)


Listen up—Malwarebytes doesn’t just talk cybersecurity, we provide it.

Protect yourself from online attacks that threaten your identity, your files, your system, and your financial well-being with our exclusive offer for Malwarebytes Premium for Lock and Code listeners.

Sextortion “help” firm took $60 million from victims, FTC alleges

15 October 2026 at 07:48

The Federal Trade Commission (FTC) has filed a complaint accusing Digital Forensics Corporation of exploiting people already targeted by sextortionists.

We have talked about sextortion and recovery scams in the past, but we never looked specifically at the combination. Apparently, there is a lot of money to be made for those ruthless enough to take money from victims already in a state of panic.

The FTC has accused Digital Forensics Corporation, its owner Dmitry Belkin, and affiliated companies of misleading sextortion victims into paying at least $60 million for assistance that, in numerous instances, they did not provide. A federal court has temporarily halted the defendants’ activities while the case proceeds.

Most of the time, sextortion emails are a bluff sent to a large number of targets to see if one takes the bait. But sextortion can also involve intimate images that someone really possesses. In those cases, a criminal threatens to share the material unless the victim pays, sends more images, or complies with other demands.

In those cases, victims can feel desperate, especially when the demands keep coming, and may look for help to make it stop. According to the FTC, Digital Forensics targeted people searching for that help through advertisements on Google, YouTube, X, and other platforms. The company allegedly claimed it could track down criminals worldwide, identify perpetrators, and provide law enforcement with evidence needed to make arrests.

Digital Forensics allegedly charged between $1,499 and $20,000 for a “Phase 1” package. That was supposed to include communicating with the sextortionist, tracking their location, producing an investigative report, and reporting the crime to law enforcement.

According to the FTC, Digital Forensics Corporation changed the victims’ account settings to block the sextortionist, fabricated chat transcripts, and presented pre-saved coordinates, often in Nigeria or the Philippines, as the sextortionist’s location.

After collecting the first payment, the company allegedly pressured customers to purchase “Phase 2” services, supposedly providing ongoing account monitoring and further assistance. The FTC says the company did not follow through on those promises either.

Another huge red flag was that the company also allegedly discouraged victims from blocking their blackmailers, contrary to law enforcement and expert advice.

The allegations against Digital Forensics Corporation have not yet been decided by the court.

How to stay safe

Be wary of anyone who promises to stop the threats or pressures you to pay immediately. Help should offer clear information and realistic options. It should not turn your fear into another payment deadline.

If someone is threatening to share intimate images, you do not have to handle it alone.

  • Preserve the threats and account details. Keep the messages, usernames, and payment demands. Block the offender but do not delete your account or the messages, since they may help real investigators.
  • Stop communicating and block the blackmailer. Do not pay them or give them access to your devices or financial accounts. Report the account using the platform’s safety tools.
  • Tell someone you trust about the sextortion. A friend, family member, counselor, or other trusted adult can provide support while you decide what to do next.
  • Report the crime. Contact local police. In the US, you can also report sextortion to the FBI. If it involves a minor, report it through the National Center for Missing and Exploited Children’s CyberTipline.

If you have already paid a service that you believe misled you, keep its ads, messages, contract, and receipts, and report your experience to the FTC through ReportFraud.ftc.gov.

If you’re unsure whether something is a scam or not, ask Malwarebytes Scam Guard. It can help you assess it and provide advice on next steps.


Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

Global Crackdown on West African Crime Networks Leads to 58 Arrests

26 August 2026 at 04:12

West African Organized Crime Groups

An eight-month international operation targeting West African organized crime groups has resulted in 58 arrests and the identification of 263 suspects across 22 countries, according to INTERPOL. Operation Jackal IV, conducted from November 2025 to June 2026, focused on disrupting criminal networks, tracing illicit funds, identifying high-value targets and supporting arrests and prosecutions. The operation brought together countries across six continents to tackle the growing global threat posed by West African criminal networks, including Black Axe and similar groups. These networks have been linked to a significant share of global cyber-enabled financial fraud, including romance scams, cryptocurrency and investment scams, and business email compromise fraud.

Operation Jackal IV Targets West African Organized Crime Groups

Operation Jackal IV also targeted money laundering activities used to move and conceal criminal proceeds across borders. INTERPOL coordinated cross-border intelligence sharing, analysis and operational support during the operation. It also provided specialized training to strengthen international investigations into financial crime. Tomonobu Kaya, Director of the INTERPOL Financial Crime and Anti-Corruption Centre, said the operation showed the importance of international cooperation in following illicit financial flows and disrupting criminal networks. [caption id="attachment_113806" align="aligncenter" width="600"]West African Organized Crime Groups Image Source: INTERPOL[/caption]

Major Arrests and Financial Crime Investigations

In Argentina, authorities identified 196 individuals linked to a major Crime-as-a-Service network suspected of providing website domains and money laundering support to West African organized crime groups. The investigation resulted in 17 arrests, with an INTERPOL Operational Support Team assisting with analysis of seized data and identification of suspects and criminal networks. South African authorities raided seven locations in Johannesburg linked to a syndicate involved in romance and investment scams targeting retirees in English-speaking countries. Investigators arrested 39 people, seized USD 2.67 million and blocked 257 bank accounts. In Italy, investigators identified an individual connected to a pan-European money laundering network that used shell companies, remittance services and cash withdrawals. One account processed EUR 845,000, or about USD 736,000, through 560 transactions involving 20 financial instruments. Romanian authorities dismantled a criminal group operating an investment scam through a call centre. The group promoted high returns from stocks and cryptocurrencies, with victims' money transferred to electronic wallets controlled by perpetrators. Authorities estimated that EUR 143 million had been stolen and laundered globally. Eleven people were arrested, while cash, cryptocurrency, six real estate properties and luxury watches were seized.

Sextortion and Crime-as-a-Service Emerge

Beyond individual investigations, the operation highlighted emerging threats involving sextortion and Crime-as-a-Service. INTERPOL identified an increase in West African organized crime groups using sextortion to target minors, including victims as young as 14. In these cases, offenders typically contacted minors through social media, established trust and persuaded them to share explicit images or videos. They then threatened to distribute the material to the victim's contacts unless a ransom was paid. Investigators also found that some criminal syndicates were procuring Crime-as-a-Service from external providers, including through the dark web. These services were used to outsource activities such as money laundering and other operational functions. While several cases from Operation Jackal IV remain under investigation, the preliminary results demonstrate the scale and international reach of the networks targeted during the eight-month operation. The participating countries were Austria, Argentina, Australia, Canada, Côte d'Ivoire, France, Germany, Indonesia, Ireland, Italy, Japan, Malaysia, the Netherlands, Nigeria, Portugal, South Africa, Spain, Sweden, Switzerland, the United Arab Emirates, the United Kingdom and the United States.

Sextortion scammers are exploiting ShinyHunters data leaks

27 July 2026 at 11:00

Sextortion scammers are using email addresses from data leaked by the ShinyHunters hacking group to add some credibility to their feeble attempts to convince people they have embarrassing information about them.

Sextortion emails are messages claiming that the scammer recorded you through your webcam while you watched pornography and now demand payment. They have been around for years and keep evolving with small changes in wording and fake technical detail.

In this campaign, the scammers pretend to be ShinyHunters. What hasn’t changed is the basic truth: there is no malware, no recording, and no credible evidence behind the threat. Despite seeing countless versions of these emails over the years, I’ve yet to encounter one that was backed up by the evidence the sender claimed to have.

BleepingComputer reports that ShinyHunters data leaks are fueling a $2,000 sextortion email scam and shared the following example:

Example sextortion email from ShinyHunters

“Subject: Information about your online security

Hello,

We are the ShinyHunters hacking group.
A few months ago, we gained access to your devices and started monitoring your online activities.

What happened:
We gained access to the Amtrak.com database where you have an account and easily accessed your email.
You weren’t very careful about the links you opened.
A week later, we installed an exploit on your devices, including your phone, giving us access to your microphone,
camera, keyboard, and all your data.
We have your photos, browsing history, conversations, and contact list.

Among other things, we discovered that you frequently visit adult websites and watch explicit videos.
We managed to record you and created videos of you pleasuring yourself.
With a few clicks, we can share these videos with your friends,
colleagues, and family or even make them public.

Proposal:
Send us $2000 in Bitcoin to the following wallet:
xxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxxx

We’ll delete everything immediately.
You have 48 hours from the moment you open this email.
Once the payment is received, we’ll remove the malware from your devices.”

BleepingComputer states it has seen data from the Amtrak, Hallmark, ADT, Substack, Betterment, CarGurus, Panera Bread, and McGraw Hill breaches used to target victims in this sextortion email campaign.

A California community college also issued a warning after seeing the campaign target people affected by the Canvas data breach.


Digital Footprint Scan

See if your personal data has been exposed.


They confirmed that the targeted email addresses had previously appeared in data leaked by ShinyHunters. They also contacted the group, which denied being behind the sextortion emails.

The increase to a $2,000 demand may suggest the scammers paid someone for the email lists. Although it’s more likely they simply downloaded the leaked data after ShinyHunters published it following failed extortion attempts.

A quick check of the Bitcoin address used in the email shows no activity.

blockchain report of scammer's Bitcoin address
No activity on their Bitcoin address

Let’s keep it that way. With any luck, these dungeon dwellers will eventually give up trying to scare people out of their hard-earned money.

How to react to sextortion emails

Some sextortion emails are badly written, but many have been polished by AI and look convincing. Regardless of how professional they look, they should be treated the same way: as unsubstantiated threats designed to scare victims into paying.

  • First and foremost, never reply to emails of this kind. Responding confirms that someone is actively reading messages sent to that address and may encourage further scam attempts.
  • Don’t let yourself be rushed into action. Scammers rely on the fact that you will not take the time to think this through and subsequently make mistakes. Ask for advice if you’re not sure.
  • An attachment is not proof. Most sextortion emails contain no evidence at all, and attachments are often used to deliver malware or make the threats appear more convincing.
  • If the email includes a password you’ve used before, change it immediately anywhere it’s still in use. Then enable two-factor authentication (2FA) wherever possible. If you’re having trouble keeping track of your passwords, consider using a password manager.
  • Delete the message, report it as spam, and move on.

Pro tip: Malwarebytes Scam Guard recognized this email for what it is: sextortion. It can recognize scams and advise you how to proceed.

Scam Guard recognizes this email as a sextortion scam

While these sextortion emails are almost always bluffs, if you’re concerned about webcam spying, Malwarebytes Webcam Monitoring can alert you when applications attempt to access your camera.


Scam or legit? Scam Guard knows.


Please Don’t Feed the Scattered Lapsus ShinyHunters

2 February 2026 at 11:15

A prolific data ransom gang that calls itself Scattered Lapsus ShinyHunters (SLSH) has a distinctive playbook when it seeks to extort payment from victim firms: Harassing, threatening and even swatting executives and their families, all while notifying journalists and regulators about the extent of the intrusion. Some victims reportedly are paying — perhaps as much to contain the stolen data as to stop the escalating personal attacks. But a top SLSH expert warns that engaging at all beyond a “We’re not paying” response only encourages further harassment, noting that the group’s fractious and unreliable history means the only winning move is not to pay.

Image: Shutterstock.com, @Mungujakisa

Unlike traditional, highly regimented Russia-based ransomware affiliate groups, SLSH is an unruly and somewhat fluid English-language extortion gang that appears uninterested in building a reputation of consistent behavior whereby victims might have some measure of confidence that the criminals will keep their word if paid.

That’s according to Allison Nixon, director of research at the New York City based security consultancy Unit 221B. Nixon has been closely tracking the criminal group and individual members as they bounce between various Telegram channels used to extort and harass victims, and she said SLSH differs from traditional data ransom groups in other important ways that argue against trusting them to do anything they say they’ll do — such as destroying stolen data.

Like SLSH, many traditional Russian ransomware groups have employed high-pressure tactics to force payment in exchange for a decryption key and/or a promise to delete stolen data, such as publishing a dark web shaming blog with samples of stolen data next to a countdown clock, or notifying journalists and board members of the victim company. But Nixon said the extortion from SLSH quickly escalates way beyond that — to threats of physical violence against executives and their families, DDoS attacks on the victim’s website, and repeated email-flooding campaigns.

SLSH is known for breaking into companies by phishing employees over the phone, and using the purloined access to steal sensitive internal data. In a January 30 blog post, Google’s security forensics firm Mandiant said SLSH’s most recent extortion attacks stem from incidents spanning early to mid-January 2026, when SLSH members pretended to be IT staff and called employees at targeted victim organizations claiming that the company was updating MFA settings.

“The threat actor directed the employees to victim-branded credential harvesting sites to capture their SSO credentials and MFA codes, and then registered their own device for MFA,” the blog post explained.

Victims often first learn of the breach when their brand name is uttered on whatever ephemeral new public Telegram group chat SLSH is using to threaten, extort and harass their prey. According to Nixon, the coordinated harassment on the SLSH Telegram channels is part of a well-orchestrated strategy to overwhelm the victim organization by manufacturing humiliation that pushes them over the threshold to pay.

Nixon said multiple executives at targeted organizations have been subject to “swatting” attacks, wherein SLSH communicated a phony bomb threat or hostage situation at the target’s address in the hopes of eliciting a heavily armed police response at their home or place of work.

“A big part of what they’re doing to victims is the psychological aspect of it, like harassing executives’ kids and threatening the board of the company,” Nixon told KrebsOnSecurity. “And while these victims are getting extortion demands, they’re simultaneously getting outreach from media outlets saying, ‘Hey, do you have any comments on the bad things we’re going to write about you.”

In a blog post today, Unit 221B argues that no one should negotiate with SLSH because the group has demonstrated a willingness to extort victims based on promises that it has no intention to keep. Nixon points out that all of SLSH’s known members hail from The Com, shorthand for a constellation of cybercrime-focused Discord and Telegram communities which serve as a kind of distributed social network that facilitates instant collaboration.

Nixon said Com-based extortion groups tend to instigate feuds and drama between group members, leading to lying, betrayals, credibility destroying behavior, backstabbing, and sabotaging each other.

“With this type of ongoing dysfunction, often compounding by substance abuse, these threat actors often aren’t able to act with the core goal in mind of completing a successful, strategic ransom operation,” Nixon wrote. “They continually lose control with outbursts that put their strategy and operational security at risk, which severely limits their ability to build a professional, scalable, and sophisticated criminal organization network for continued successful ransoms – unlike other, more tenured and professional criminal organizations focused on ransomware alone.”

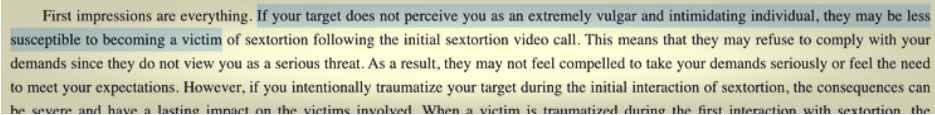
Intrusions from established ransomware groups typically center around encryption/decryption malware that mostly stays on the affected machine. In contrast, Nixon said, ransom from a Com group is often structured the same as violent sextortion schemes against minors, wherein members of The Com will steal damaging information, threaten to release it, and “promise” to delete it if the victim complies without any guarantee or technical proof point that they will keep their word. She writes:

A key component of SLSH’s efforts to convince victims to pay, Nixon said, involves manipulating the media into hyping the threat posed by this group. This approach also borrows a page from the playbook of sextortion attacks, she said, which encourages predators to keep targets continuously engaged and worrying about the consequences of non-compliance.

“On days where SLSH had no substantial criminal ‘win’ to announce, they focused on announcing death threats and harassment to keep law enforcement, journalists, and cybercrime industry professionals focused on this group,” she said.

An excerpt from a sextortion tutorial from a Com-based Telegram channel. Image: Unit 221B.

Nixon knows a thing or two about being threatened by SLSH: For the past several months, the group’s Telegram channels have been replete with threats of physical violence against her, against Yours Truly, and against other security researchers. These threats, she said, are just another way the group seeks to generate media attention and achieve a veneer of credibility, but they are useful as indicators of compromise because SLSH members tend to name drop and malign security researchers even in their communications with victims.

“Watch for the following behaviors in their communications to you or their public statements,” Unit 221B’s advisory reads. “Repeated abusive mentions of Allison Nixon (or “A.N”), Unit 221B, or cybersecurity journalists—especially Brian Krebs—or any other cybersecurity employee, or cybersecurity company. Any threats to kill, or commit terrorism, or violence against internal employees, cybersecurity employees, investigators, and journalists.”

Unit 221B says that while the pressure campaign during an extortion attempt may be traumatizing to employees, executives, and their family members, entering into drawn-out negotiations with SLSH incentivizes the group to increase the level of harm and risk, which could include the physical safety of employees and their families.

“The breached data will never go back to the way it was, but we can assure you that the harassment will end,” Nixon said. “So, your decision to pay should be a separate issue from the harassment. We believe that when you separate these issues, you will objectively see that the best course of action to protect your interests, in both the short and long term, is to refuse payment.”

❌