❌

Normal view

Nottinghamshire police officer in hospital after being shot in the foot

Large cordon in place around Angel Row area of city centre after ‘shocking incident’ in the early hours of Sunday

A police officer is in hospital after being shot in the foot in Nottingham in the early hours of Sunday.

Nottinghamshire police said the officer had approached two suspects in the city centre when he was struck by a bullet. The force said the two suspects, a woman and a man, had fled the scene and were being sought by police.

Continue reading...

© Photograph: Joe Giddens/PA

© Photograph: Joe Giddens/PA

© Photograph: Joe Giddens/PA

UK police force pays out after claims it protected officers accused of abusing women

Exclusive: Devon and Cornwall police formally apologise to nine women and settle claim without admitting liability

A police force alleged to have promoted and protected male officers despite knowing they were accused of domestic abuse has formally apologised and paid compensation to nine women, the Guardian has learned.

The women allege they were subjected to a range of abuse including rape, assault, threats, harassment and coercive control while in relationships with male officers from Devon and Cornwall police.

Continue reading...

© Photograph: Andrew Lloyd/Alamy

© Photograph: Andrew Lloyd/Alamy

© Photograph: Andrew Lloyd/Alamy

Number of cloned number plates on UK roads at record high, data shows

More than 11,400 drivers last year were fined for offences they did not recognise as RAC says system needs reform

The number of reported “cloned” vehicles involved in offences on UK roads has reached a record high, official data shows.

More than 11,400 drivers contacted the DVLA last year after being issued with fines for offences they said they did not recognise or accept responsibility for – most of which are believed to be down to cloning, where a number plate is copied fraudulently on similar vehicles to avoid enforcement cameras.

Continue reading...

© Photograph: Anthony Smith/Alamy

© Photograph: Anthony Smith/Alamy

© Photograph: Anthony Smith/Alamy

Rebellion review – story of Bradford 12 revisits Britain’s ugly racist past

15 October 2026 at 06:08

Ken Fero and Tariq Mehmood’s documentary recalls the fight against racism in 1980s Britain – even if its account of solidarity has a notable omission

This fierce film from socialist film-makers Ken Fero and Tariq Mehmood gives us the story and the context of the Bradford 12. Twelve south Asian members of the United Black Youth League in 1981 were arrested on a charge of conspiracy to cause explosions for possessing dozens of molotov cocktails – milk bottles filled with petrol, with a rag through the lid – allegedly for throwing at the police. To the intense irritation of the British authorities, a mixed-race jury acquitted them, accepting their argument that it was in self-defence (and that the items themselves were closer to fireworks than bombs), because black and Asian communities were routinely and systematically attacked by skinheads and racists whose activities were shrugged at by the powers that be.

It is a reminder of a particularly ugly, squalid, bigoted and mediocre era in British public life, when Margaret Thatcher, just before becoming prime minister, tried to siphon off some of the far-right National Front’s political energy by declaring that people felt “swamped” by immigrants, the most earsplittingly loud dog whistle in Tory history. It was also the era when anti-racist protester Blair Peach was killed by the Met’s yet-to-be-disbanded special patrol group, when the still-unsolved New Cross fire in London took the lives of 13 young black people, when the south Asian woman Anwar Ditta was subject to a spitefully obstructive move from the Home Office to prevent her bringing her children into the UK – supposedly because they weren’t really hers, though a DNA test finally proved her right. Perhaps most of all, it was an era when the witness-box testimony of uniformed police officers was increasingly seen as almost valueless in these cases; the film also reminds us how culpably lackadaisical and incompetent the Yorkshire police were in catching the serial killer Peter Sutcliffe.

Continue reading...

© Photograph: ©migrant media/ishaq kazi

© Photograph: ©migrant media/ishaq kazi

© Photograph: ©migrant media/ishaq kazi

Palantir and Sadiq Khan drop legal battle over Met contract

14 October 2026 at 12:05

Dispute related to claims London mayor blocked US tech firm from £50m police deal because of concerns over its values

Palantir and the London mayor, Sadiq Khan, have called off their legal fight over claims the Labour mayor was blocking the US tech company from signing a contract with the Metropolitan police because of its values and ethics.

Palantir and the mayor’s office for policing and crime (Mopac) announced on Wednesday they had withdrawn allegations against each other, heading off a high court trial scheduled for January.

Continue reading...

© Photograph: Justin Tallis/Reuters

© Photograph: Justin Tallis/Reuters

© Photograph: Justin Tallis/Reuters

How Europe’s most wanted cocaine trafficker turned Sierra Leone into the world’s first true narco state

14 October 2026 at 02:00

Drawing on dozens of interviews with intelligence and police officers across two continents, a Guardian investigation reveals the murderous cost of our insatiable appetite for cocaine

Read more: Latin American organised crime ‘may operate in 16 European countries’
Explainer:
What is state capture and why does it matter?

As abductions go, few have been more brazen. Alan Jalloh was with two friends outside Goodies supermarket, frantic as usual with late afternoon shoppers. Rush hour in downtown Freetown, Sierra Leone’s capital, was under way with familiar gusto.

A black Toyota Rav4 forced its way through the Peninsula highway traffic. Witnesses describe burly white men leaping out, yanking on balaclavas. Jalloh, 40, seemed to freeze. As did his two friends, one a famous Freetown footballer. All three were dragged into the waiting SUV. None of them have been seen since.

Continue reading...

© Composite: Guardian Design

© Composite: Guardian Design

© Composite: Guardian Design

Barriers facing black and south Asian music events ‘cost London up to £141m a year’

Exclusive: Investigation finds racial inequality in live music industry rife and many genres labelled ‘high risk’ despite lack of evidence

Black and south Asian music events in London face disproportionate cancellations, restrictions and licensing barriers compared with white events, according to a two-year investigation into racial inequality in the capital’s live music industry.

The Race Equality in Music Event Licensing (REMEL) report, led by Black Lives in Music, estimates that cancellations, displacement and events prevented from taking place cost London £127m to £141m annually, with projected losses exceeding £650m over five years.

Continue reading...

© Photograph: Kingsley Davis/Alamy Stock Photo/Alamy Live News.

© Photograph: Kingsley Davis/Alamy Stock Photo/Alamy Live News.

© Photograph: Kingsley Davis/Alamy Stock Photo/Alamy Live News.

Mahmood orders urgent security review after killing of Ann Widdecombe

12 October 2026 at 14:20

Home secretary also expands police support ‘with immediate effect’ for high-profile public figures not currently MPs

Security arrangements for high-profile public figures including politicians and members of the royal family are to be urgently reviewed after the killing of Ann Widdecombe, the home secretary has said.

Shabana Mahmood said former MPs, party leaders who are not MPs, peers, former members of devolved parliaments and party spokespeople will also be offered police support.

Continue reading...

© Photograph: Dan Kitwood/Reuters

© Photograph: Dan Kitwood/Reuters

© Photograph: Dan Kitwood/Reuters

Police officer injured as 10 arrests made at tense Liverpool v Manchester City match

12 October 2026 at 09:54
  • Police officer taken to hospital with serious facial injury

  • Five people arrested on suspicion of tragedy chanting

A police officer sustained a serious facial injury while making an arrest after the Liverpool v Manchester City match at Anfield on Sunday, Merseyside police have said.

The fixture was highly charged as City played their first match since it was confirmed they had been found guilty of breaching Premier League financial rules.

Continue reading...

© Photograph: Adam Vaughan/EPA

© Photograph: Adam Vaughan/EPA

© Photograph: Adam Vaughan/EPA

Met chief says ‘toxicity’ around DEI will not stop him recruiting more black and Asian officers

Mark Rowley says inclusivity is crucial for the force and he refuses to be ‘blown off course’ by critics

Mark Rowley has said the Metropolitan police must recruit more black and Asian officers in order to gain the trust of minority ethnic communities in London, and vowed not to be “blown off course by the culture wars”.

The right has criticised drives for diversity, claiming they lead to lower standards. Rowley, who is commissioner of the Met and Britain’s top police officer, said that as a leader of a major organisation he was prepared to take a stand against the “toxicity” surrounding the diversity debate and criticised other leaders for “running away from the subject”.

Continue reading...

© Photograph: Thomas Krych/Story Picture Agency/Shutterstock

© Photograph: Thomas Krych/Story Picture Agency/Shutterstock

© Photograph: Thomas Krych/Story Picture Agency/Shutterstock

I will have more police officers of colour in the UK capital – and the culture wars won’t stop me doing it | Mark Rowley

12 October 2026 at 01:00

In our major recruitment drive, the focus must be on underrepresented communities. It is not favouritism, it is fairness – and it’s essential

Effective policing depends upon inclusivity. If you are committed to policing by consent that stands or falls on the trust of all communities, you cannot do without it.

Last Monday, we launched a major recruitment campaign. We have no interest in the politics and ideologies of the culture wars. Inclusion is an operational necessity.

Mark Rowley is commissioner of the Metropolitan police

Do you have an opinion on the issues raised in this article? If you would like to submit a response of up to 300 words by email to be considered for publication in our letters section, please click here.

Continue reading...

© Photograph: Stefan Rousseau/PA

© Photograph: Stefan Rousseau/PA

© Photograph: Stefan Rousseau/PA

Alleged abuse victims at British military school in Germany tell of agonising fight for justice

10 October 2026 at 05:00

Two women, now in their 50s, say MoD refuses to take responsibility for abuse they suffered as children

Anne and Jane* were 10 years old when a member of staff connected with their British military school in Bünde, Germany is alleged to have singled them out and sexually abused them.

Now in their 50s, the women say he coerced them into keeping silent, and for decades they had only discussed their experiences with one another. “He said if we ever told anybody, then our fathers would lose their jobs and they would be kicked out of the army,” Jane said. “Being two young 10-year-old girls who basically followed their fathers around the world, their jobs were our lives.”

Continue reading...

© Composite: Guardian Design/Getty Images

© Composite: Guardian Design/Getty Images

© Composite: Guardian Design/Getty Images

Palantir’s Tom Watson says ‘mob rule’ must not dictate awarding of government contracts

9 October 2026 at 03:20

Former Labour deputy leader says tech firm would work with a Reform UK government on immigration crackdowns

Tom Watson, the former Labour deputy leader who recently joined Palantir, has warned against “mob rule” when it comes to awarding public contracts.

Lord Watson, now a senior vice-president at the US tech corporation, said UK ministers could get themselves “in a lot of trouble” as he was questioned about concerns raised about the government working with his new employer.

Continue reading...

© Photograph: Oli Scarff/AFP/Getty Images

© Photograph: Oli Scarff/AFP/Getty Images

© Photograph: Oli Scarff/AFP/Getty Images

Search warrants used in Andrew Mountbatten-Windsor raids were unlawful, court rules

8 October 2026 at 12:23

‘Technical errors’ are embarrassing for Thames Valley police but unlikely to affect outcome of investigation

Andrew Mountbatten-Windsor has won his legal challenge against Thames Valley police over search warrants used to raid his home after they arrested him.

The former prince brought a judicial review of the legality of the force’s actions and those of the central criminal court, which granted the warrants.

Continue reading...

© Photograph: Shutterstock

© Photograph: Shutterstock

© Photograph: Shutterstock

‘Entitled’ ex-police chief guilty of gross misconduct over affairs with junior officers

8 October 2026 at 11:11

Scott Chilton, who led Hampshire and the Isle of Wight police, barred from becoming a police officer again

A former chief constable showed a sense of entitlement, dishonesty and lack of integrity by having sexual relationships with two subordinate officers, including engaging in sexual activity while on call to lead major incidents, a misconduct hearing has ruled.

The panel found that the behaviour of Scott Chilton, 53, who retired as chief constable of Hampshire and the Isle of Wight before the hearing, amounted to gross misconduct.

Continue reading...

© Photograph: Steve Parsons/PA

© Photograph: Steve Parsons/PA

© Photograph: Steve Parsons/PA

Police routinely failing to investigate ‘revenge porn’ in England and Wales

7 October 2026 at 04:00

Lawyers launch super-complaint after research shows officers frequently dismiss image-based abuse

Police forces are routinely failing to investigate complaints about the circulation of image-based abuse, previously known as “revenge pornography”, according to research that has triggered a super-complaint over the way such crimes are handled.

Lawyers have gathered evidence from 100 people who reported intimate images being shared online without their consent. Their research suggests that image-based abuse is still frequently dismissed or not recognised as criminal offending, despite being described by the former prime minister Keir Starmer as a national emergency.

Continue reading...

© Photograph: Microgen Images/SCIENCE PHOTO LIBRARY/Getty Images/Science Photo Library RF

© Photograph: Microgen Images/SCIENCE PHOTO LIBRARY/Getty Images/Science Photo Library RF

© Photograph: Microgen Images/SCIENCE PHOTO LIBRARY/Getty Images/Science Photo Library RF

Possible Vulnerability in Apple’s Automatic Reboot

6 October 2026 at 07:06

404Media is reporting (alternate link) that a cyber-weapons arms manufacturer is exploiting a vulnerability in iOS to bypass its automatic reboot security feature. This is the feature that automatically puts an iPhone into a more secure state if it hasn’t been used for 72 hours.

The new technology to get around inactivity reboot was developed by Magnet Forensics, the company behind GrayKey, a popular tool sold to law enforcement agencies that allows them to unlock and access data stored in iPhones and Android smartphones. Magnet has developed a new device called GrayKey Preserve and a feature for its regular GrayKey devices called Evidence Preservation Mode, according to the video.

“This is an absolute game changer for iOS forensics and a function that I wish we had years ago,” a Magnet employee says in the leaked video, specifically mentioning that the solution is targeted at the iPhone’s inactivity reboot feature and the data it makes unavailable. GrayKey Preserve and Evidence Preservation Mode are also designed to combat another iPhone feature that automatically deletes certain data ­- such as cached locations, and recently deleted photos and iMessages ­- after a certain number of days. “We’re gonna be able to preserve that data for an infinite amount of time.”

Presumably, now that Apple engineers know that this flaw exists they can find and fix it. AI turns out to be really good at this sort of thing.

Another news article.

‘It could knock a whole street down’: the art of defusing a second world war bomb

6 October 2026 at 00:00

On 14 January this year, army and navy squads faced an unprecedented challenge: one bomb on a Plymouth building site, another floating on a dredger in Exmouth. That afternoon, the clock started ticking

Everyone at Exmouth Marina knew there was an unexploded German bomb in the water. Old hands at the dock had been saying so since the end of the second world war. But the marina had been dredged and re-dredged and nothing had ever come up. It had started to sound like an old wives’ tale. The marina is a busy stretch of water: a commercial port until the late 1990s that had since been converted into a home to private yachts. A bomb, you’d think, would have a hard time staying hidden. But in the middle of the afternoon on Wednesday 14 January 2026, 81 years after the end of the second world war, Steve Hockings-Thompson, the manager of Exmouth Marina, got a call from the crew of a dredging vessel telling him he’d better come out to the boat. “I thought: ‘Oh crikey. We’ve got a bit of an issue here,’” Hockings-Thompson told me recently.

He went out to the dredger, a squat barge that hauls silt and other debris from the marina floor on to a flat deck that resembles a steel sieve. Sitting on the deck was a huge hunk of metal, caked in mud and stones. As Hockings-Thompson got closer and saw its distinctive conical shape, he knew it was a bomb – a big one. The dredger was loaded with 20,000 litres of diesel fuel, so if the bomb detonated, it would be disastrous. He called the police, who quickly came to the scene. “And then,” he said, “all hell broke loose.”

Continue reading...

© Photograph: Sam Frost/The Guardian

© Photograph: Sam Frost/The Guardian

© Photograph: Sam Frost/The Guardian

Using Device Linking to Eavesdrop on WhatsApp and Signal

29 September 2026 at 07:02

Modern messaging apps allow users to link their phone accounts to their computer desktop. Eavesdroppers are taking advantage of this capability:

Apps such as WhatsApp Web and Signal Desktop allow people to use their accounts on other devices, such as laptops or desktop computers.

Germany’s Customs Office has been using these features to connect a police-controlled computer to a suspect’s account.

Once connected, messages can be delivered to that computer without the police having to crack the encryption protecting them.

Netzpoltik details that police are able to gain access in this way either through physical access to someone’s phone or by intercepting verification codes via a state-sanctioned phishing attack or intercepting SMS messages via telephone surveillance.

That last paragraph is important. Making this work requires user consent.

What we want is a feature that displays connected devices, so users could notice if a new device gets connected to their account.

The A.I. Party House Where Networking Has a Dark Side

21 September 2026 at 11:37
Group tech houses have proliferated across the San Francisco Bay Area in the artificial intelligence boom. One of the most prominent has also racked up an extensive police record.

© Minh Connors for The New York Times

The entrance to AGI House in Hillsborough, Calif. AGI House is one of the most prominent and notorious tech group homes in the artificial intelligence boom.

Tumbler Ridge Shooting Survivors File 30 Lawsuits Against OpenAI

4 September 2026 at 13:19
The survivors contend that the company should have notified the police when it shut down the shooter’s disturbing ChatGPT account eight months before the February attack in British Columbia.

© Paige Taylor White/Agence France-Presse — Getty Images

A memorial for the victims of a deadly mass shooting at a school in Tumbler Ridge, British Columbia, in February.

Police Are Hiding Their Use of Flock Surveillance Cameras

20 August 2026 at 05:48

A usage policy for Flock license plate reader cameras tells police not to talk about the cameras:

When cops use Flock to arrest someone in Wapello County, Iowa, they don’t want them to know. A usage policy for the automated license plate reader cameras in the county tells police, in no uncertain terms, to keep them a secret: “DO NOT MENTION ALPR USAGE TO THE OCCUPANTS OF THE VEHICLE,” the policy document reads. “DO NOT MENTION ALPR USAGE IN YOUR REPORT OR COMPLAINT UNLESS ABSOLUTELY NECESSARY.”

This reminds me of IMSI-catchers (Stingray was the most popular) a couple of decades ago. Police would go to even more extremes to hide their usage.

PNLD Data Breach Exposes Police and Government Contact Details on Dark Web

PNLD data breach

The PNLD data breach has exposed contact information belonging to police officers, government partners, criminal justice professionals and customers after data from the Police National Legal Database (PNLD) was published on the dark web. The data breach at PNLD, identified on July 26, 2026, also affected some users of Ask the Police, raising concerns about targeted phishing attacks. 

PNLD Data Breach Exposes Police and Contact Details 

According to PNLD, the compromised data includes names, organizations and work email addresses of police officers, police staff, criminal justice professionals, government partners and customers. The incident also exposed the names and email addresses of some individuals who had previously submitted questions through Ask the Police. UK government guidance warns that such information could enable attackers to craft more convincing phishing emails targeting named officers and affected individuals.  In its official statement, PNLD said, "There is no evidence to suggest that passwords or other security credentials have been compromised." The organisation clarified that it provides legal information, products and services to UK police forces and criminal justice organisations. It also stressed that PNLD is not the Police National Computer or the Police National Database, is not a crime-recording system, and does not store confidential information relating to victims, witnesses or offenders. 

PNLD Notifies Authorities and Affected Users 

Following the PNLD data breach, the organization said it had contacted all affected organizations and provided additional guidance. Individuals impacted through Ask the Police have also received notification emails with further information PNLD confirmed that it has informed the Information Commissioner's Office (ICO) and is working with the National Crime Agency (NCA) and specialist cybersecurity organizations as the investigation continues.  Its statement noted: "We are continuing to investigate a data security incident affecting the Police National Legal Database (PNLD), which was identified on Sunday 26 July." It added that compromised information had been published on the dark web and reiterated that there is no evidence that passwords or other security credentials were accessed.  Regarding Ask the Police, PNLD said the platform was affected because it is hosted on the same infrastructure, resulting in the publication of some users' names and email addresses. 

Investigation Continues as Key Questions Remain 

As of August 3, 2026, PNLD had not disclosed how many people were affected by the data breach at PNLD, when the intrusion began, how long unauthorized access lasted or the total volume of data obtained. Its public breach notice lists the categories of exposed information but does not include a victim count.  PNLD's 2025-26 annual summary reported 108,429 police registrations and support for all 43 Home Office police forces. However, the organization emphasized that this figure represents its user base and should not be interpreted as the number of people affected by the breach.  The organization's 2023-24 annual summary stated that PNLD uses Microsoft Power Platform technology. On August 3, 2026, The Hacker News reported that the breach notification page referenced assets hosted on Microsoft's content.powerapps.com domain. While this supports the platform connection, it does not indicate how the attackers accessed or extracted the compromised data. 

Dubai Police Warns Against Online Scams Promising Work and Visit Visas

Dubai Police fraudulent visa ads

The Dubai Police fraudulent visa ads warning has cautioned the public against scams offering work visas, residency visas, and visit visas in exchange for money. According to the Anti Fraud Centre at Dubai Police's General Department of Criminal Investigation, fraudsters are using social media platforms and messaging apps to circulate fake visa offers by impersonating official entities or using the names of unlicensed companies. The advisory was issued as part of Dubai Police's Be Aware of Fraud campaign, which aims to raise awareness about online scams and help residents identify fraudulent schemes.

Dubai Police Fraudulent Visa Ads Circulating on Social Media

According to Dubai Police, scammers are promoting visa services through advertisements and messages that claim to offer work, residency, or visit visas for a fee. The Anti Fraud Centre said these advertisements are designed to convince victims to transfer money by falsely claiming to represent government authorities or licensed visa service providers. Some also use the names of unlicensed companies or offices to appear legitimate. Dubai Police urged the public not to rely on such offers and reminded residents that all visa procedures should be completed only through competent authorities or legally approved offices.

Authorities Urge Public to Verify Visa Offers

The Anti Fraud Centre said verifying the source of a visa service is the first step in avoiding visa fraud. Residents have been advised to confirm the authenticity of any visa offer or application process through official channels before making payments or sharing personal information. The centre also warned against dealing with intermediaries or unknown individuals claiming they can arrange visas through unofficial means. Dubai Police said people should not be misled by promises of guaranteed visas or job opportunities that are offered outside the legal process.

How to Report Fraud Attempts

Dubai Police has asked members of the public to report any fraud or attempted fraud immediately. Reports can be submitted through the Dubai Police Smart App, the eCrime platform for cybercrime reports, or by calling 901. The Anti Fraud Centre reiterated that staying informed and verifying service providers through official channels remain the most effective ways to avoid falling victim to fraudulent visa schemes.

Dutch Police Arrest Key Suspect in €100M Global Crypto Investment Scam

global crypto investment scam

A major global crypto investment scam investigation has led to the arrest of an alleged key figure behind an international criminal organization accused of defrauding victims of more than €100 million every month. Dutch police announced multiple arrests across Europe following a long-running investigation into a fraud network that allegedly employed over 700 people operating from around 20 call centers worldwide.

The main suspect, a 46-year-old dual Israeli and Polish national, was arrested at an airport in Poland on May 26 at the request of Dutch authorities. Investigators believe he played an indispensable role in the organization, which allegedly carried out large-scale investment fraud targeting victims across multiple countries.

Global Crypto Investment Scam Network Operated Through Worldwide Call Centers

According to Dutch police, the organization functioned like a professional company with approximately 700 employees spread across nearly 20 offices globally. Individuals working as financial advisors scam operators allegedly contacted victims daily through online platforms and telephone calls while posing as legitimate investment professionals.

Authorities said the organization was structured with a central headquarters overseeing multiple teams, each assigned to target victims in specific countries. Employees reportedly worked under pseudonyms and used technical measures to hide their identities and locations.

[caption id="attachment_113134" align="aligncenter" width="600"]global crypto investment scam Excerpts from emails that victims sent to scammers[/caption]

As part of the investigation, Belgian police arrested five individuals believed to have worked as fraudulent financial advisors.

Multiple Arrests Made Across Europe

The investigation resulted in several coordinated arrests during May and July.

On July 7, authorities arrested two Dutch nationals aged 45 and 34, along with a 34-year-old Belgian, all residing in Cyprus. A 25-year-old suspect was also arrested in Belgium the same day. On July 10, police arrested a 44-year-old Dutch national in Athens.

The main suspect has since been extradited to the Netherlands, where an examining magistrate ordered 14 days of pre-trial detention. Dutch authorities indicated that additional arrests remain possible as the investigation continues.

How the Global Crypto Investment Scam Worked

Investigators said the online investment scam relied on building long-term trust with victims. Individuals posing as account managers or financial advisors maintained frequent contact through phone calls and online communication, sometimes over several months.

Victims were encouraged to begin with relatively small investments that appeared to generate immediate returns. Police said the investment platforms displayed convincing but fabricated profits, even though no actual investments were being made.

As confidence grew, victims were persuaded to transfer increasingly larger amounts, often in the form of cryptocurrency fraud payments. Instead of being invested, investigators said the funds were diverted directly to the criminal organization.

Authorities also warned that victims who stop investing may later be contacted by so-called recovery companies requesting upfront deposits to recover lost funds. Police believe these recovery operations may also be connected to the same fraud networks.

Hundreds of Complaints Linked to Investment Fraud

Dutch authorities have received approximately 550 reports connected to the organization, while Belgian police have recorded around 200 complaints. Investigators estimate the total number of victims worldwide could reach tens of thousands.

The financial losses reported by victims in the Netherlands alone amount to nearly €25 million, with many individuals losing well over €10,000.

Dutch police said officers proactively contacted some victims after discovering that many remained unaware they had fallen victim to cyber fraud.

Financial investigators are now examining whether assets linked to the suspects can be frozen or seized.

Digital Infrastructure Taken Offline

Investigators said the criminal organization remained active since at least 2021 and relied heavily on concealed digital infrastructure to evade law enforcement.

By tracing financial transactions, IP addresses, and other digital evidence, the Dutch police identified offices, suspects, and critical infrastructure supporting the operation. Authorities worked with commercial service providers to take key elements of the network offline.

The investigation also involved Europol, with intelligence shared across multiple countries to support ongoing criminal prosecutions.

Officials said the case demonstrates the scale and sophistication of modern investment fraud operations and highlighted continued international cooperation to dismantle cyber-enabled financial crime networks.

Alleged Kimwolf Botmaster ‘Dort’ Arrested, Charged in U.S. and Canada

21 May 2026 at 17:50

Canadian authorities on Wednesday arrested a 23-year-old Ottawa man on suspicion of building and operating Kimwolf, a fast spreading Internet-of-Things botnet that enslaved millions of devices for use in a series of massive distributed denial-of-service (DDoS) attacks over the past six months. KrebsOnSecurity publicly named the suspect in February 2026 after the accused launched a volley of DDoS, doxing and swatting campaigns against this author and a security researcher. He now faces criminal hacking charges in both Canada and the United States.

A criminal complaint unsealed today in an Alaska district court charges Jacob Butler, a.k.a. “Dort,” of Ottawa, Canada with operating the Kimwolf DDoS botnet. A statement from the Department of Justice says the complaint against Butler was unsealed following the defendant’s arrest in Canada by the Ontario Provincial Police pursuant to a U.S. extradition warrant. Butler is currently in Canadian custody awaiting an initial court hearing scheduled for early next week.

The government said Kimwolf targeted infected devices which were traditionally “firewalled” from the rest of the internet, such as digital photo frames and web cameras. The infected systems were then rented to other cybercriminals, or forced to participate in record-smashing DDoS attacks, as well as assaults that affected Internet address ranges for the Department of Defense. Consequently, the DoD’s Defense Criminal Investigative Service is investigating the case, with assistance from the FBI field office in Anchorage.

“KimWolf was tied to DDoS attacks which were measured at nearly 30 Terabits per second, a record in recorded DDoS attack volume,” the Justice Department statement reads. “These attacks resulted in financial losses which, for some victims, exceeded one million dollars. The KimWolf botnet is alleged to have issued over 25,000 attack commands.”

On March 19, U.S. authorities joined international law enforcement partners in seizing the technical infrastructure for Kimwolf and three other large DDoS botnets — named Aisuru, JackSkid and Mossad — that were all competing for the same pool of vulnerable devices.

On February 28, KrebsOnSecurity identified Butler as the Kimwolf botmaster after digging through his various email addresses, registrations on the cybercrime forums, and posts to public Telegram and Discord servers. However, Dort continued to threaten and harass researchers who helped track down his real-life identity and dramatically slow the spread of his botnet.

Dort claimed responsibility for at least two swatting attacks targeting the founder of Synthient, a security startup that helped to secure a widespread critical security weakness that Kimwolf was using to spread faster and more effectively than any other IoT botnet out there. Synthient was among many technology companies thanked by the Justice Department today, and Synthient’s founder Ben Brundage told KrebsOnSecurity he’s relieved Butler is in custody.

“Hopefully this will end the harassment,” Brundage said.

An excerpt from the criminal complaint against Butler, detailing how he ordered a swatting attack against Ben Brundage, the founder of the security firm Synthient.

The government says investigators connected Butler to the administration of the KimWolf botnet through IP address, online account information, transaction records, and online messaging application records obtained through the issuance of legal process. The criminal complaint against Butler (PDF) shows he did little to separate his real-life and cybercriminal identities (something we demonstrated in our February unmasking of Dort).

In April, the Justice Department joined authorities across Europe in seizing domain names tied to nearly four-dozen DDoS-for-hire services, although because of a bureaucratic mix-up the list of seized domains has remain sealed until today. The DOJ said at least one of those services collaborated with Butler’s Kimwolf botnet.

A statement from the Ontario Provincial Police said a search warrant was executed on March 19 at Butler’s address in Ottawa, where they seized multiple devices. As a result of that investigation, Butler was arrested and charged this week with unauthorized user of computer; possession of device to obtain unauthorized use of computer system or to commit mischief; and mischief in relation to computer data. He is scheduled to remain in custody until a hearing on May 26.

In the United States, Butler is facing one count of aiding and abetting computer intrusion. If extradited, tried and convicted in a U.S. court, Butler could face up to 10 years in prison, although that maximum sentence would likely be heavily tempered by considerations in the U.S. Sentencing Guidelines, which make allowances for mitigating factors such as youth, lack of criminal history and level of cooperation with investigators.

Germany Doxes “UNKN,” Head of RU Ransomware Gangs REvil, GandCrab

5 April 2026 at 22:07

An elusive hacker who went by the handle “UNKN” and ran the early Russian ransomware groups GandCrab and REvil now has a name and a face. Authorities in Germany say 31-year-old Russian Daniil Maksimovich Shchukin headed both cybercrime gangs and helped carry out at least 130 acts of computer sabotage and extortion against victims across the country between 2019 and 2021.

Shchukin was named as UNKN (a.k.a. UNKNOWN) in an advisory published by the German Federal Criminal Police (the “Bundeskriminalamt” or BKA for short). The BKA said Shchukin and another Russian — 43-year-old Anatoly Sergeevitsch Kravchuk — extorted nearly $2 million euros across two dozen cyberattacks that caused more than 35 million euros in total economic damage.

Daniil Maksimovich SHCHUKIN, a.k.a. UNKN, and Anatoly Sergeevitsch Karvchuk, alleged leaders of the GandCrab and REvil ransomware groups.

Germany’s BKA said Shchukin acted as the head of one of the largest worldwide operating ransomware groups GandCrab and REvil, which pioneered the practice of double extortion — charging victims once for a key needed to unlock hacked systems, and a separate payment in exchange for a promise not to publish stolen data.

Shchukin’s name appeared in a Feb. 2023 filing (PDF) from the U.S. Justice Department seeking the seizure of various cryptocurrency accounts associated with proceeds from the REvil ransomware gang’s activities. The government said the digital wallet tied to Shchukin contained more than $317,000 in ill-gotten cryptocurrency.

The GandCrab ransomware affiliate program first surfaced in January 2018, and paid enterprising hackers huge shares of the profits just for hacking into user accounts at major corporations. The GandCrab team would then try to expand that access, often siphoning vast amounts of sensitive and internal documents in the process. The malware’s curators shipped five major revisions to the GandCrab code, each corresponding with sneaky new features and bug fixes aimed at thwarting the efforts of computer security firms to stymie the spread of the malware.

On May 31, 2019, the GandCrab team announced the group was shutting down after extorting more than $2 billion from victims. “We are a living proof that you can do evil and get off scot-free,” GandCrab’s farewell address famously quipped. “We have proved that one can make a lifetime of money in one year. We have proved that you can become number one by general admission, not in your own conceit.”

The REvil ransomware affiliate program materialized around the same as GandCrab’s demise, fronted by a user named UNKNOWN who announced on a Russian cybercrime forum that he’d deposited $1 million in the forum’s escrow to show he meant business. By this time, many cybersecurity experts had concluded REvil was little more than a reorganization of GandCrab.

UNKNOWN also gave an interview to Dmitry Smilyanets, a former malicious hacker hired by Recorded Future, wherein UNKNOWN described a rags-to-riches tale unencumbered by ethics and morals.

“As a child, I scrounged through the trash heaps and smoked cigarette butts,” UNKNOWN told Recorded Future. “I walked 10 km one way to the school. I wore the same clothes for six months. In my youth, in a communal apartment, I didn’t eat for two or even three days. Now I am a millionaire.”

As described in The Ransomware Hunting Team by Renee Dudley and Daniel Golden, UNKNOWN and REvil reinvested significant earnings into improving their success and mirroring practices of legitimate businesses. The authors wrote:

“Just as a real-world manufacturer might hire other companies to handle logistics or web design, ransomware developers increasingly outsourced tasks beyond their purview, focusing instead on improving the quality of their ransomware. The higher quality ransomware—which, in many cases, the Hunting Team could not break—resulted in more and higher pay-outs from victims. The monumental payments enabled gangs to reinvest in their enterprises. They hired more specialists, and their success accelerated.”

“Criminals raced to join the booming ransomware economy. Underworld ancillary service providers sprouted or pivoted from other criminal work to meet developers’ demand for customized support. Partnering with gangs like GandCrab, ‘cryptor’ providers ensured ransomware could not be detected by standard anti-malware scanners. ‘Initial access brokerages’ specialized in stealing credentials and finding vulnerabilities in target networks, selling that access to ransomware operators and affiliates. Bitcoin “tumblers” offered discounts to gangs that used them as a preferred vendor for laundering ransom payments. Some contractors were open to working with any gang, while others entered exclusive partnerships.”

REvil would evolve into a feared “big-game-hunting” machine capable of extracting hefty extortion payments from victims, largely going after organizations with more than $100 million in annual revenues and fat new cyber insurance policies that were known to pay out.

Over the July 4, 2021 weekend in the United States, REvil hacked into and extorted Kaseya, a company that handled IT operations for more than 1,500 businesses, nonprofits and government agencies. The FBI would later announce they’d infiltrated the ransomware group’s servers prior to the Kaseya hack but couldn’t tip their hand at the time. REvil never recovered from that core compromise, or from the FBI’s release of a free decryption key for REvil victims who couldn’t or didn’t pay.

Shchukin is from Krasnodar, Russia and is thought to reside there, the BKA said.

“Based on the investigations so far, it is assumed that the wanted person is abroad, presumably in Russia,” the BKA advised. “Travel behaviour cannot be ruled out.”

There is little that connects Shchukin to UNKNOWN’s various accounts on the Russian crime forums. But a review of the Russian crime forums indexed by the cyber intelligence firm Intel 471 shows there is plenty connecting Shchukin to a hacker identity called “Ger0in” who operated large botnets and sold “installs” — allowing other cybercriminals to rapidly deploy malware of their choice to thousands of PCs in one go. However, Ger0in was only active between 2010 and 2011, well before UNKNOWN’s appearance as the REvil front man.

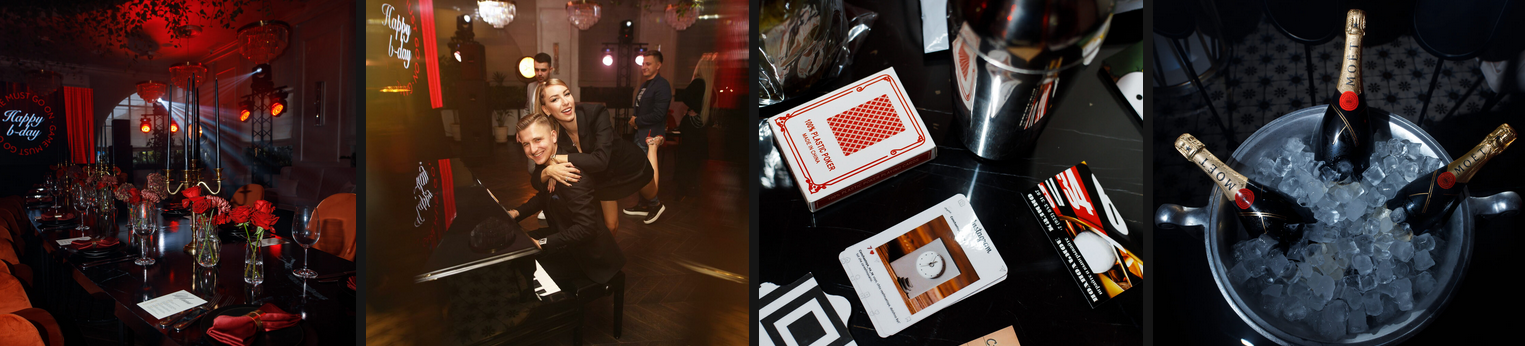
A review of the mugshots released by the BKA at the image comparison site Pimeyes found a match on this birthday celebration from 2023, which features a young man named Daniel wearing the same fancy watch as in the BKA photos.

Images from Daniil Shchukin’s birthday party celebration in Krasnodar in 2023.

Update, April 6, 12:06 p.m. ET: A reader forwarded this English-dubbed audio recording from a ccc.de (37C3) conference talk in Germany from 2023 that previously outed Shchukin as the REvil leader (Shchuckin is mentioned at around 24:25).

❌